Aperture GA: Tailscale's key-free gateway for agents
- Source
- tailscale.com
- Author
- Tailscale
- Date
Context
Tailscale has made Aperture generally available, and its case is that an can use models and work on your network without anyone handing it an API key. Aperture started as a proxy for model requests: engineers and agents on a tailnet, the private Tailscale network their devices join, sent requests through it, so the keys stayed with the gateway instead of being copied to each person and agent. Tailscale says it has since grown into a gateway with cost controls, , logging and a proxy for MCP servers, the Model Context Protocol tool interfaces that agents call, which keeps still more keys away from agents and people.
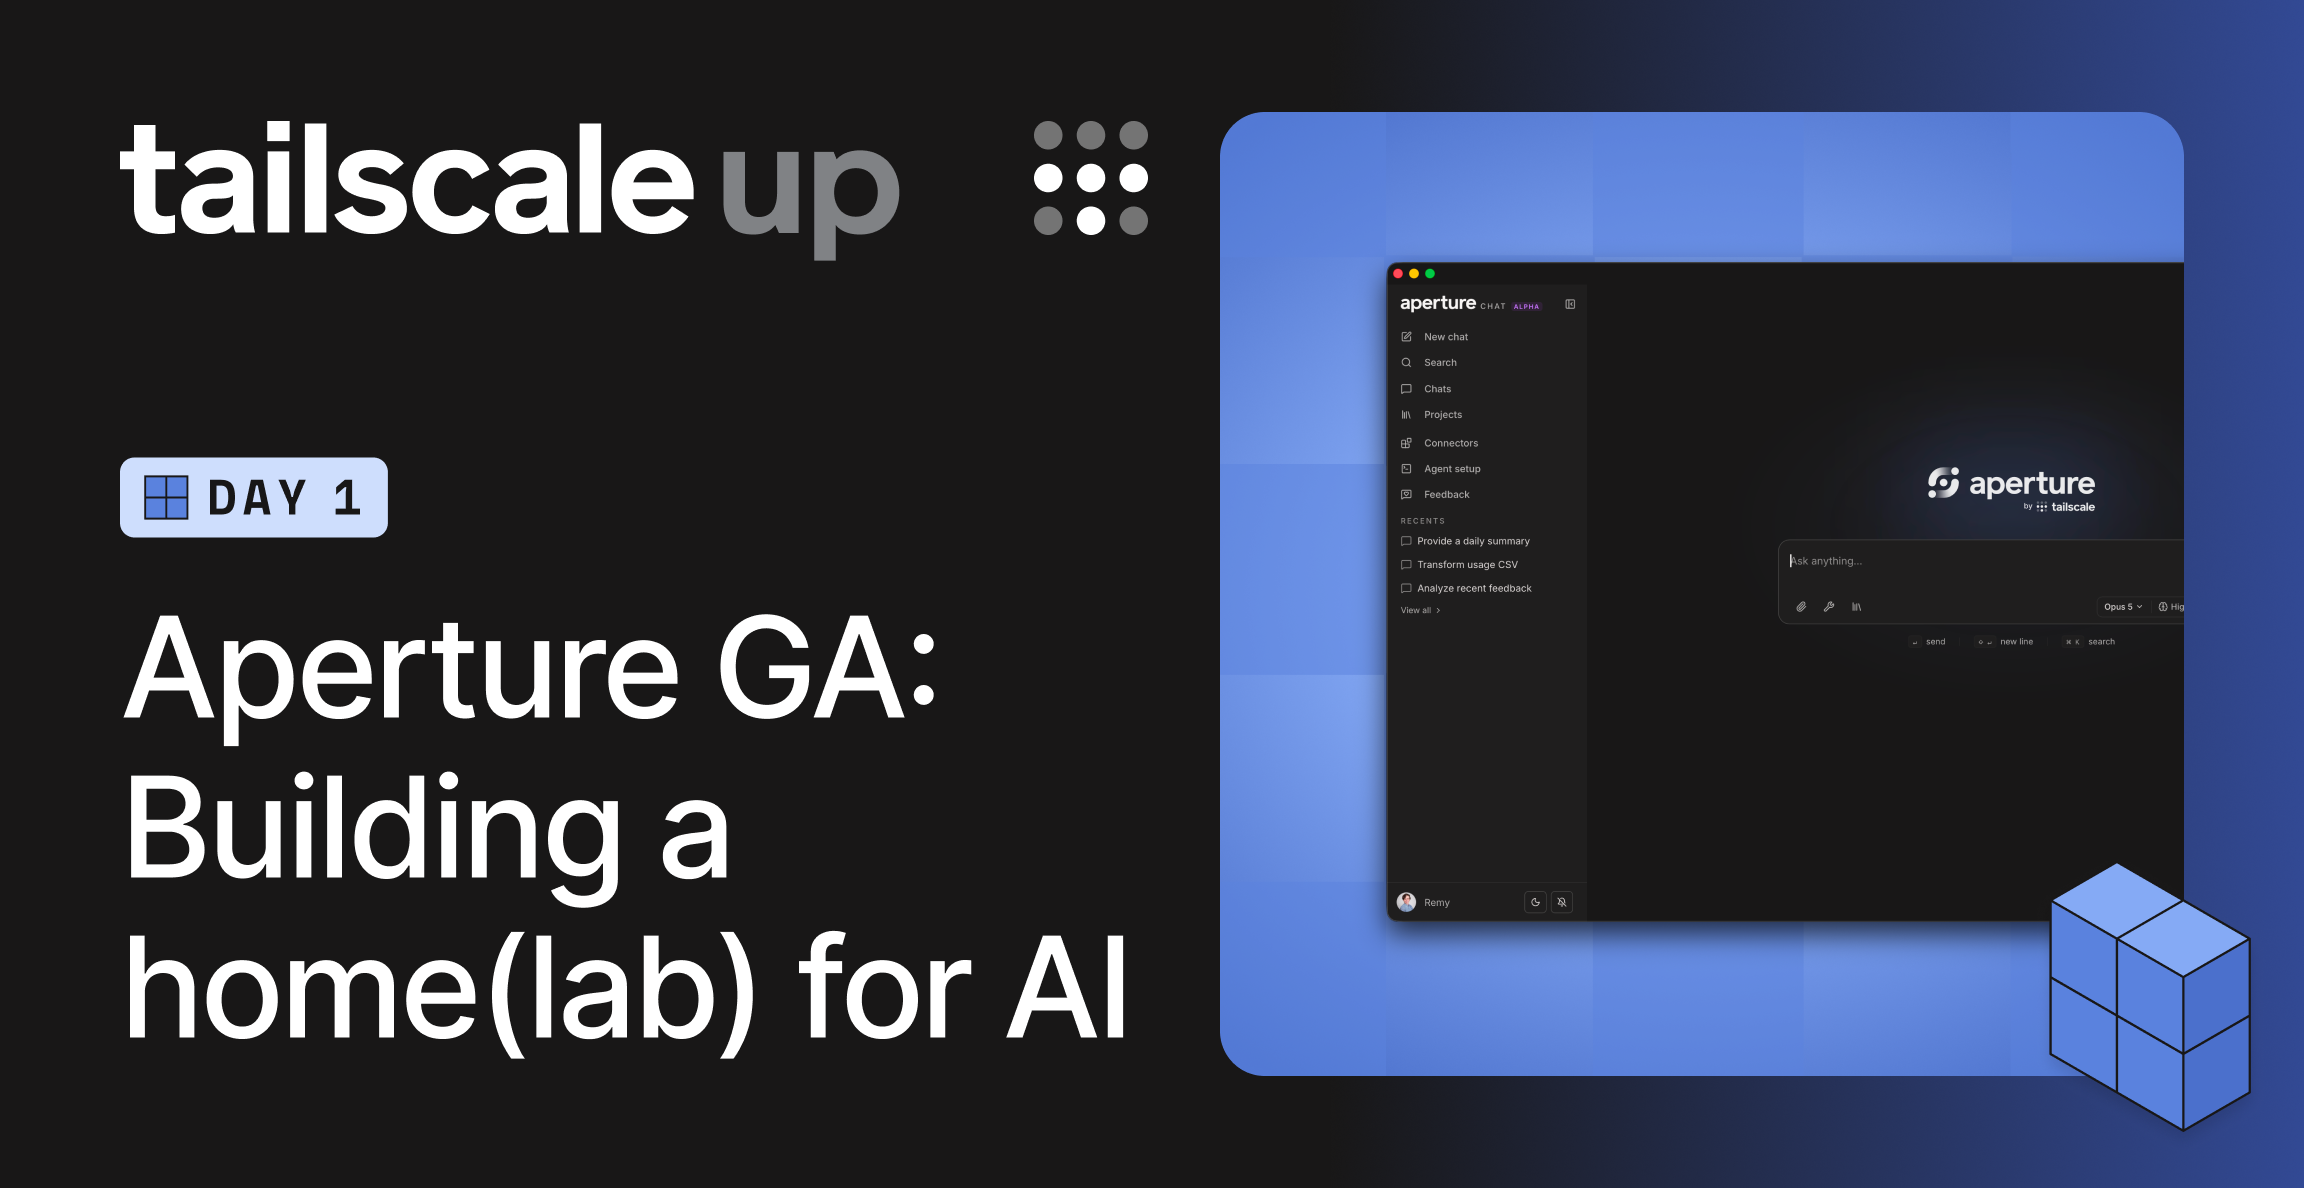
The general-availability announcement highlights three additions. New Aperture instances come with some tokens included, and more can be bought for major and closed models inside Aperture, where previously an open-weight model needed a third-party API key or expensive hardware of your own. Two new MCP endpoints, Tailscale and Tailscale SSH, let Aperture and coding agents add machines to the tailnet and reach them over Tailscale SSH. In Tailscale's example, an agent deploying a service asks you for access and, once you approve, configures it without you copying keys or filling in environment variables. The chat interface also gains Projects, which share instructions, tool access and tailnet machines across related chats, and default that carry across every chat.
The controls on that agent come from the network, not from the agent. Tailscale names three: agents working through Aperture must obey the tailnet's access control rules, which decide which machines can talk to Aperture and which it can reach; you approve every machine Aperture wants to add; and every agent action is logged. What changes with this release is where an agent's reach is defined. It is set by the tailnet's access rules, which the owner already manages, and by the owner's approval of each machine, rather than by credentials pasted into the agent's environment. These are Tailscale's descriptions of its own design.
- AI agent — An AI system that doesn't just answer once but works toward a goal in a loop — taking actions, reading the results, and deciding what to do next.
- guardrails — The checks around a model that block bad inputs and outputs — filters, validators, and permission rules the model itself can't override.
- open weights — A model whose trained parameters are published for anyone to download and run — unlike API-only models you can access but never possess.
- tool permissions — The rules governing which tools an agent may call and which need confirmation — the boundary between a mistake and an incident.

Checking sign-in…
Loading comments…