Depglobe
depglobe.pages.dev- Category
- Cybersecurity
- Rank
- No. 132Apps board
Previous survey · No. 122 ·
- Pricing
- Open Source
- Type
- TOOL
- Date
About
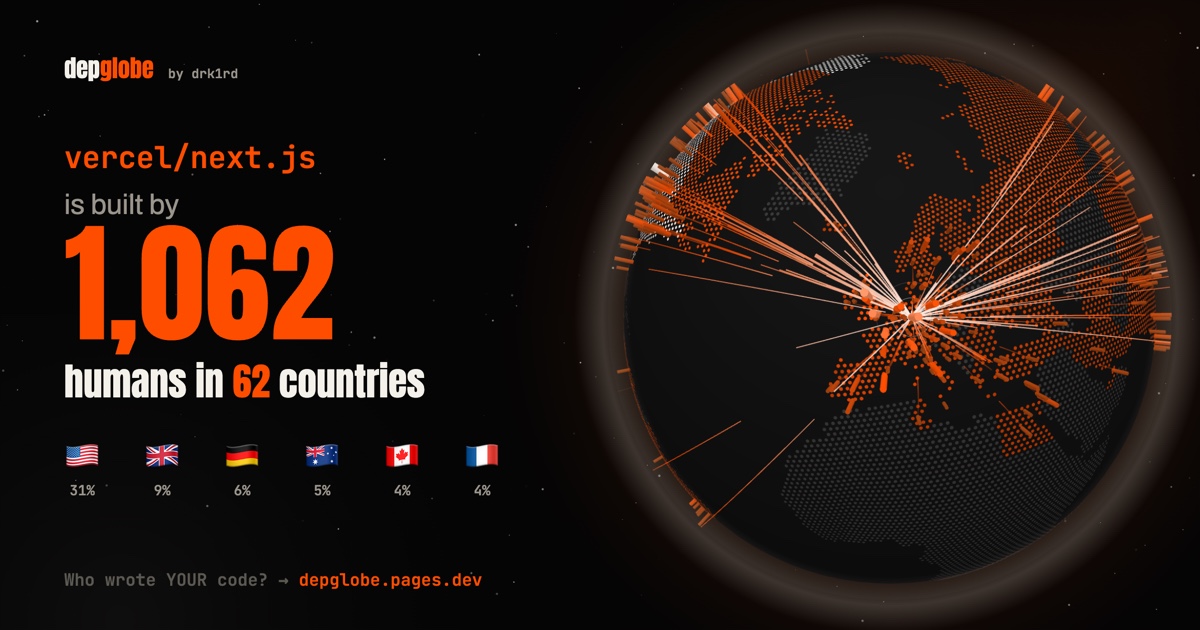
Depglobe is a browser-based tool that traces a GitHub repository's dependency tree across npm, PyPI, Go, Cargo, Maven, RubyGems, NuGet, Composer, and GitHub Actions, then plots the maintainers behind those packages on a 3D globe by country. It runs entirely client-side, requires no token for standard scans, and accepts an optional GitHub token to scan more packages and recent commits faster.
At a glance
Depglobe takes a GitHub repository and maps people it associates with its dependencies. It is worth opening when you want to see who is behind a project’s packages and pick a few upstream repositories to explore.
Good fit
Open-source maintainers and developers curious about the people and packages upstream of a public GitHub project.
Consider something else when
Skip it if you need a complete dependency inventory, verified maintainer locations or a security assessment for release approval.
Start here
Enter a small public GitHub repository with a package manifest. After scanning, open Packages and compare an entry against the upstream project before drawing conclusions from its map pin.
Cost and requirements
The developer offers a browser scan of public repositories without a token. Optional Turbo mode requests a GitHub token and can remember it in the browser. Start without one.
Limits to know
The developer lists a 200-package cap for an unauthenticated scan and 400 with Turbo. Coverage and maintainer locations were reviewed from the project’s description.
Sources checked 2026-11-05. Source-based assessment.
Why it made the leaderboard
Turns an abstract dependency list into an explorable map of who actually maintains your supply chain, making geographic concentration risk visible and easy to share.
Tags
Media
Comments (0)
No comments yet
Editorially curated, with community endorsements as a secondary signal. Corrections welcome.