GitHub Copilot Local Sandboxing Is Now Generally Available
- Source
- github.blog
- Author
- GitHubTop Viber
- Date
Local sandboxing changes the default risk of letting Copilot run commands on a developer machine. Instead of inheriting the user's full environment, commands execute in isolation, and access to files, network, system capabilities and credentials is granted at a granular level. Enterprises can set these policies centrally rather than relying on each developer's configuration. The feature reaches all three Copilot surfaces at once, so teams do not need different rules for the CLI and the editor. It also matters for model choice: GitHub launched Haiku 5.5 the same day and positioned it for terminal tasks and subagents, exactly the workloads that run many small commands. Teams that held back on agent command execution over credential exposure now have a supported control to evaluate.
Context
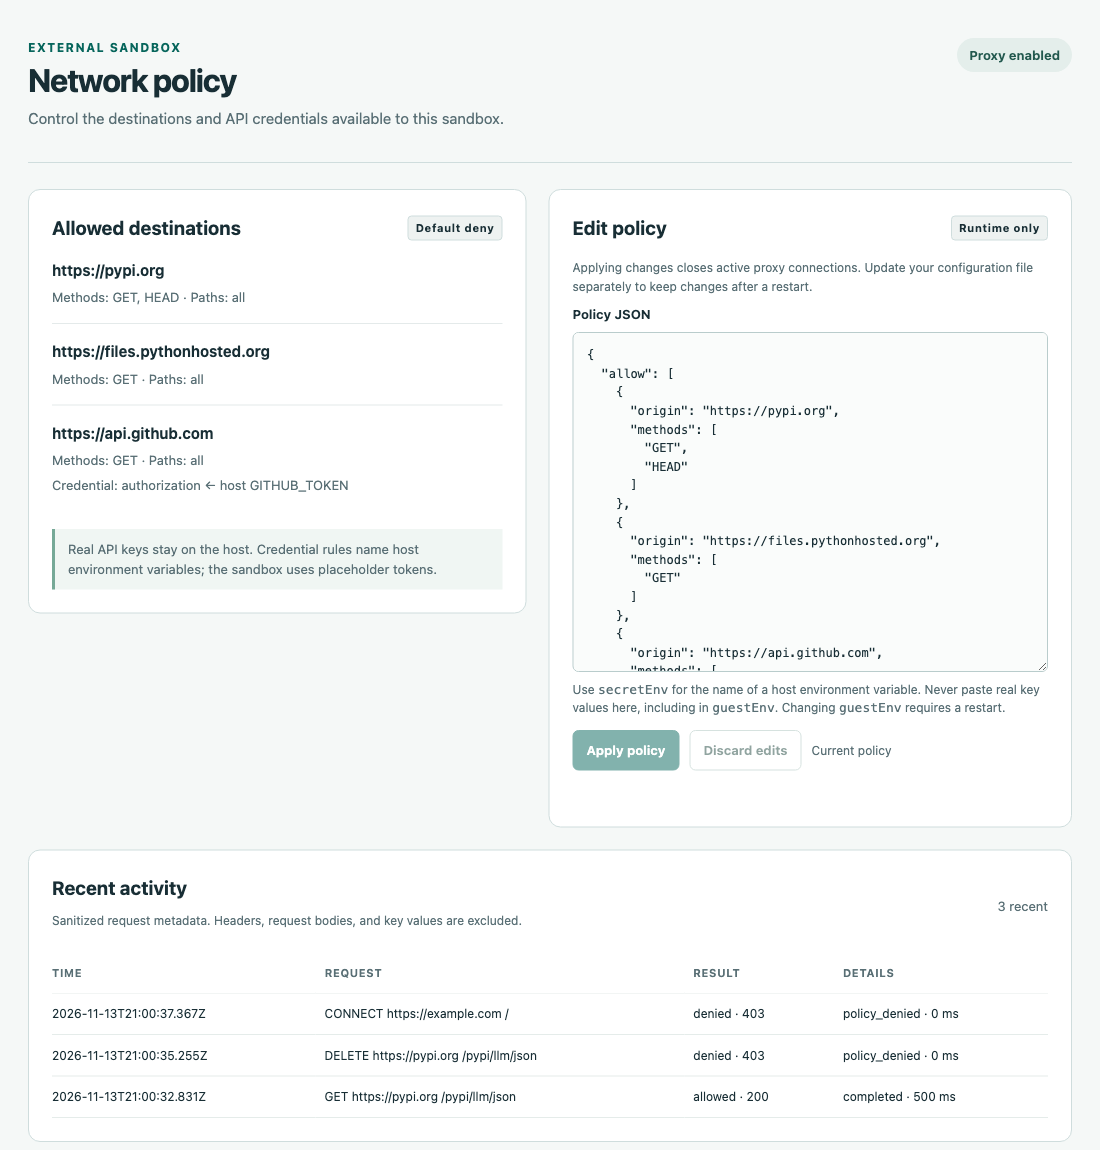
When an AI agent works on a developer's own computer, the commands and tools it starts act on that computer. GitHub has now made local sandboxing generally available for Copilot in the Copilot CLI, the Copilot app and VS Code sessions using Agent Host. According to the changelog, tools and commands Copilot initiates run with restricted access to the filesystem, network, credentials and other system capabilities, under policies set by the developer or their organization. Policies can limit which files and directories agent-run commands can read or change. They can also control access to the internet, local networks, credentials and GitHub CLI credentials, and can extend to local tools such as servers and language servers where supported.
The sandbox is built on Microsoft eXecution Container, or MXC, which takes one common sandbox policy and translates it into each operating system's native controls on Windows, macOS and Linux, so the same rules can follow a developer across machines. For companies, the key part is that enterprise-managed settings can require sandboxing and enforce policies developers cannot weaken. GitHub also separates the model from the : sandbox policies apply to tool execution regardless of which model Copilot is using. The feature is included with Copilot at no extra cost.
The changelog is a short release note. It does not say which native mechanism each operating system uses, whether protection is equally strong on all three, or whether sandboxing is on by default. For those details it points readers to GitHub's About cloud and local sandboxes documentation, which this explanation does not draw on. Intel earlier covered GitHub's guide to using local sandboxing in the Copilot CLI, which covers using the feature from the .
- Git and version control — A system for recording and comparing changes to a codebase.
- Model Context Protocol (MCP) — A published agreement for an AI application to discover what a separate program offers and ask it to run one of those offerings.
- Boundary — A point in a program where one part finishes its job and hands its result to another.
- Terminal and shell — A text interface for navigating files and running programs.

Checking sign-in…
Loading comments…