Shipping 11x more code with agents outpaces human security review. Shopify describes attack surface maps, focused AI reviews and checks that grow with each fixed vulnerability as a way to keep up.
Key takeaways · AI-distilled
Shopify says its mobile code output is about 11x a year earlier: roughly 434,000 lines changed per week during its 12-week Shopify app rewrite, against about 39,000 a year before. That pace, plus record vulnerability counts industry-wide, drove a new security approach.
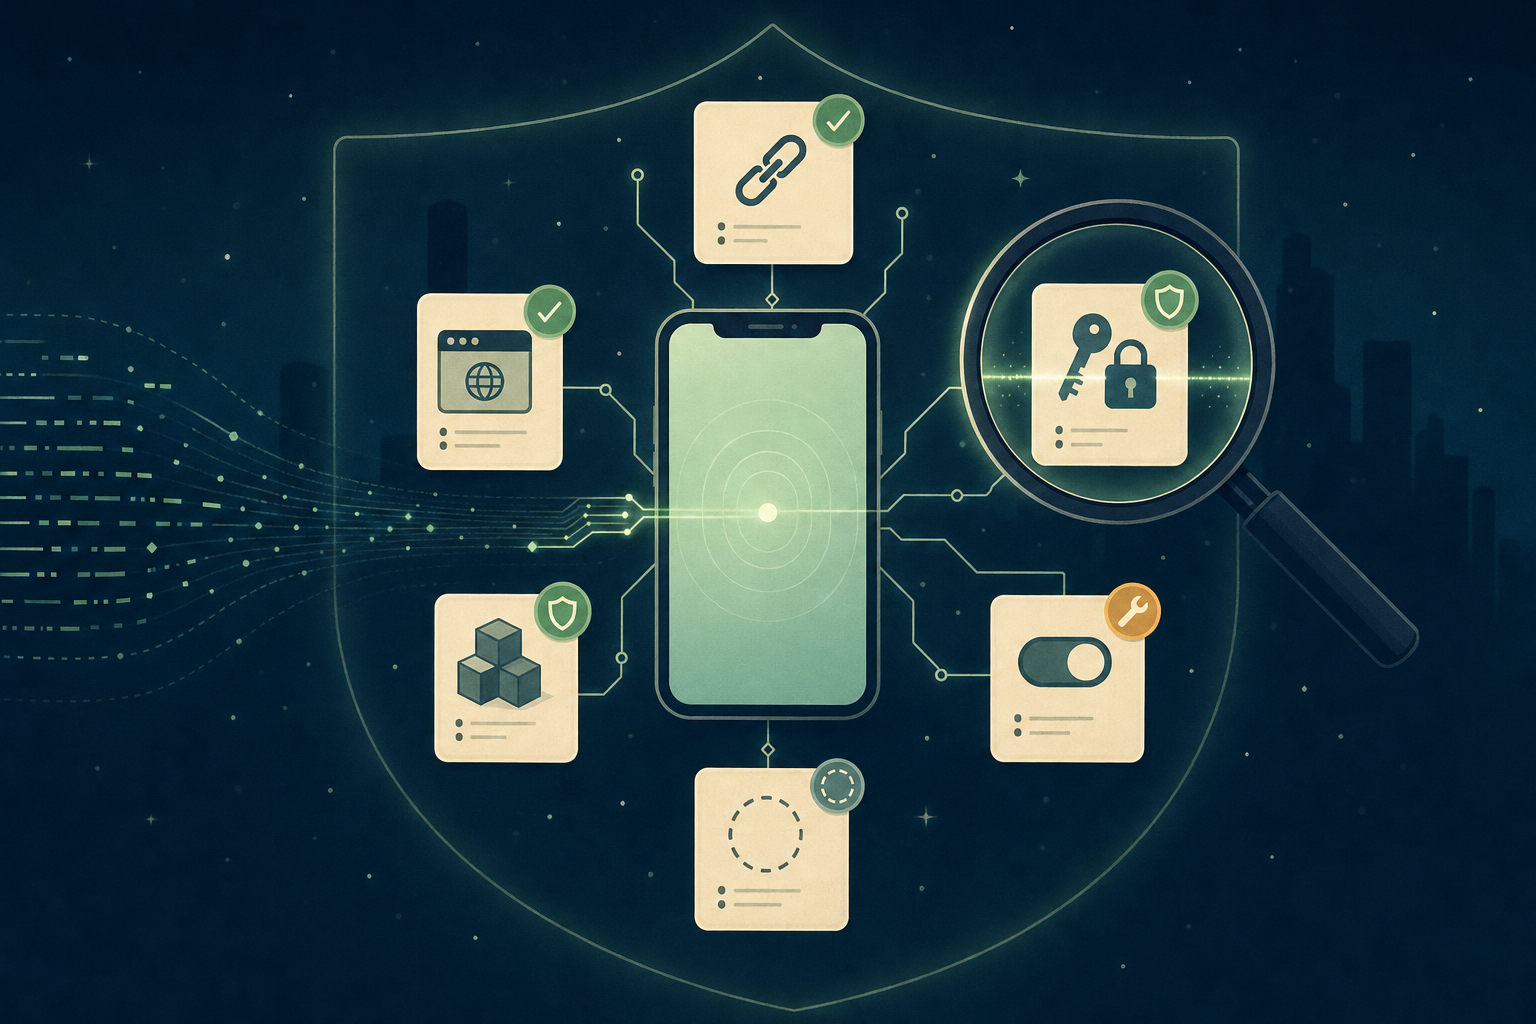
Each app has an attack surface map: security-sensitive items grouped into surfaces such as deep links, WebViews, stored data, permissions and dependencies. Every item links to its code and gets one of five verdicts: Fix (with severity), Tradeoff, Secure, Fixed or Debug only.
One agent skillA reusable instruction file that teaches an agent how to do one job well — the procedure, the tools, and what counts as done.Full definition → per surface builds the map, seeded from OWASP's MASVS and MASTG plus lessons from vulnerabilities reported against mobile apps. After each incident or HackerOne report, Shopify adds that bug class to the skills, so every later run checks the code for it.
Shopify says asking a model to find vulnerabilities in a whole app yields a long, vague list. Each skill first inventories every item, such as each deep link route and the parameters it reads, then the model reviews one item at a time with only the code it touches.
Every weekday a pipeline compares the current inventory with the last accepted map; an item counts as changed when a cited code line or its inventory entry changed. Models judge each change with read-only tools, answers are checked for format, line ranges and secrets.
Terms in this piece · Glossary
agent skill — A reusable instruction file that teaches an agent how to do one job well — the procedure, the tools, and what counts as done.