Hacktron Traces NoSQL Injection Across Novu's Codebase in 30-Day Pilot
- Source
- x.com
- Date

With the help of Hacktron, Novu catches second-order vulnerabilities across a codebase 400+ contributors touch, without adding process or noise fatigue. Around half the security issues found by Hacktron in the first 30 days were fixed, and 83% were actionable. It also found a high-severity NoSQL injection that could have led to an attacker viewing, editing, or deleting a conversation that wasn't theirs. Hacktron’s Review caught this by tracing the call chain across three files: the ingest controller that accepts the raw event payload, the type cast without deep validation, and the sink service that passes the unvalidated ID into the NoSQL query.

https://t.co/QRbs8ARNTp
Context
Hacktron AI says its automated code review tool, running against Novu, a notification infrastructure project with more than 400 contributors, found a high-severity NoSQL injection that could have let an attacker view, edit, or delete another user's conversation. The bug required following data across three points in the codebase: a controller accepting a raw incoming event payload, a type cast that converts an ID field without validating its contents, and a downstream service that passes that unvalidated ID straight into a database query. Hacktron's thread says this kind of cross-file 'second-order' vulnerability is exactly what automated review is meant to catch in a codebase too large for any one engineer to hold in their head.
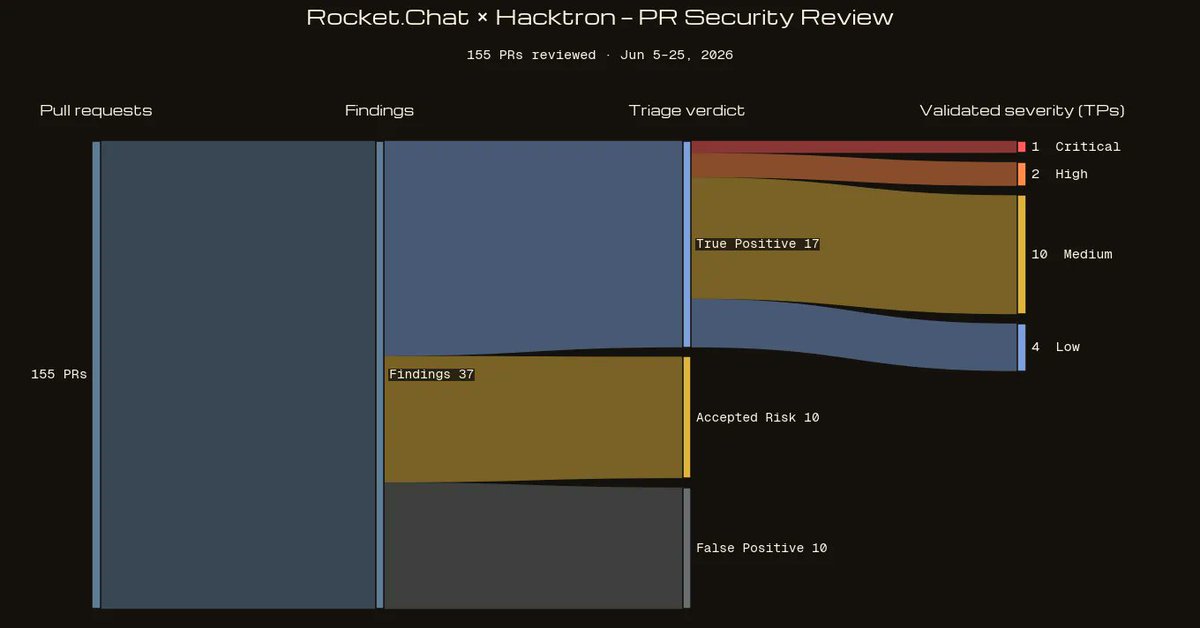
Over the pilot's first 30 days, Hacktron says roughly half of the security issues it flagged in Novu's codebase were fixed and 83 percent were judged actionable, meaning real enough to act on rather than false positives. Those percentages come from Hacktron's own reporting on its own product's pilot and were not independently verified here.
Checking sign-in…
Loading comments…