How a Vibe-Coded Dashboard's Auth Flaw Let an Attacker Drain $600K in Credits
- Source
- x.com
- Date

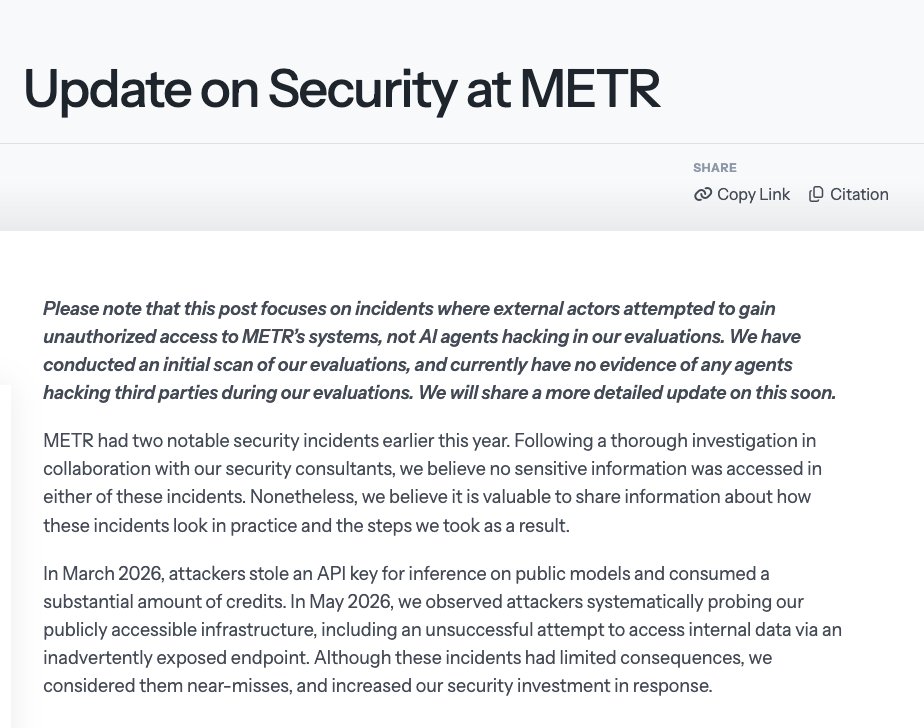
METR’s vibe-coded dashboard exposed an agent through an authentication flaw. An attacker prompted it to reveal its API key. Over three weeks, the attacker consumed roughly $600K in credits. The provider supplied them free; METR reported no financial loss. A successful login doesn’t test what happens without one. Even an HTTP 401 can hide an unauthorized action. If the backend queues work before authentication, a worker can still execute it. Check the response, queue, and task database together. Then trace which credentials the worker can read. A separate inference service can hold the provider key and enforce access and usage limits. Before you deploy: > Test that rejected requests create no jobs > Check access across different user accounts > Keep provider keys outside code-execution workers > Restrict worker permissions > Test credential revocation and recovery
Context
METR, a nonprofit that evaluates AI systems, ran an internal dashboard with an authentication flaw serious enough that an attacker could prompt the agent behind it into revealing its own API key. Independent reporting on the incident, including The Hacker News, describes the entry point as a fail-open bug that left the dashboard reachable from the public internet. Over roughly three weeks the attacker used the stolen key to run up close to $600,000 in credits; the model provider had supplied those credits for free, so METR reported no direct financial loss.
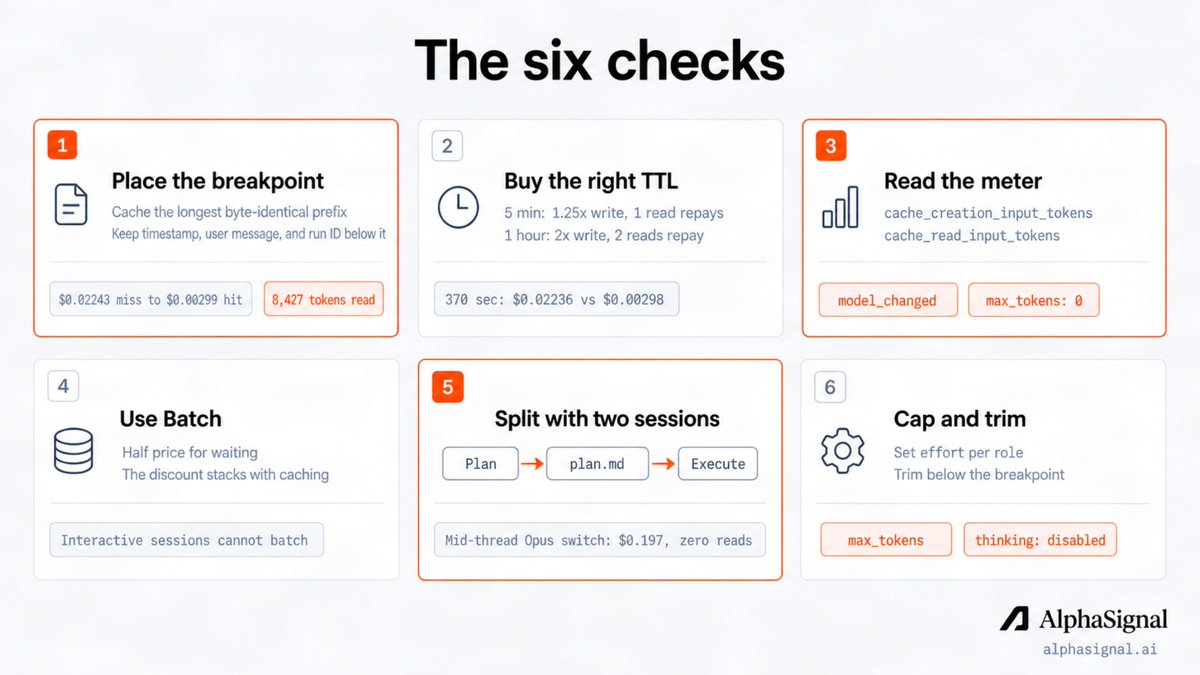
Per AlphaSignal's breakdown of the incident, the deeper lesson is that a rejected request, even one returning a clear HTTP 401, doesn't prove nothing happened: if a backend queues a task before verifying who sent it, a worker downstream can still execute that task using real credentials. AlphaSignal frames the fix as testing that rejected requests create no jobs, checking access across separate accounts, keeping provider keys out of code-execution workers, and confirming a leaked credential can actually be revoked.


Checking sign-in…
Loading comments…