AI Security Is an Engineering Problem — How to Solve It at Every Layer of the Agent Stack
Source
blogs.nvidia.com
Author
Saša Zdjelar
Date
Context
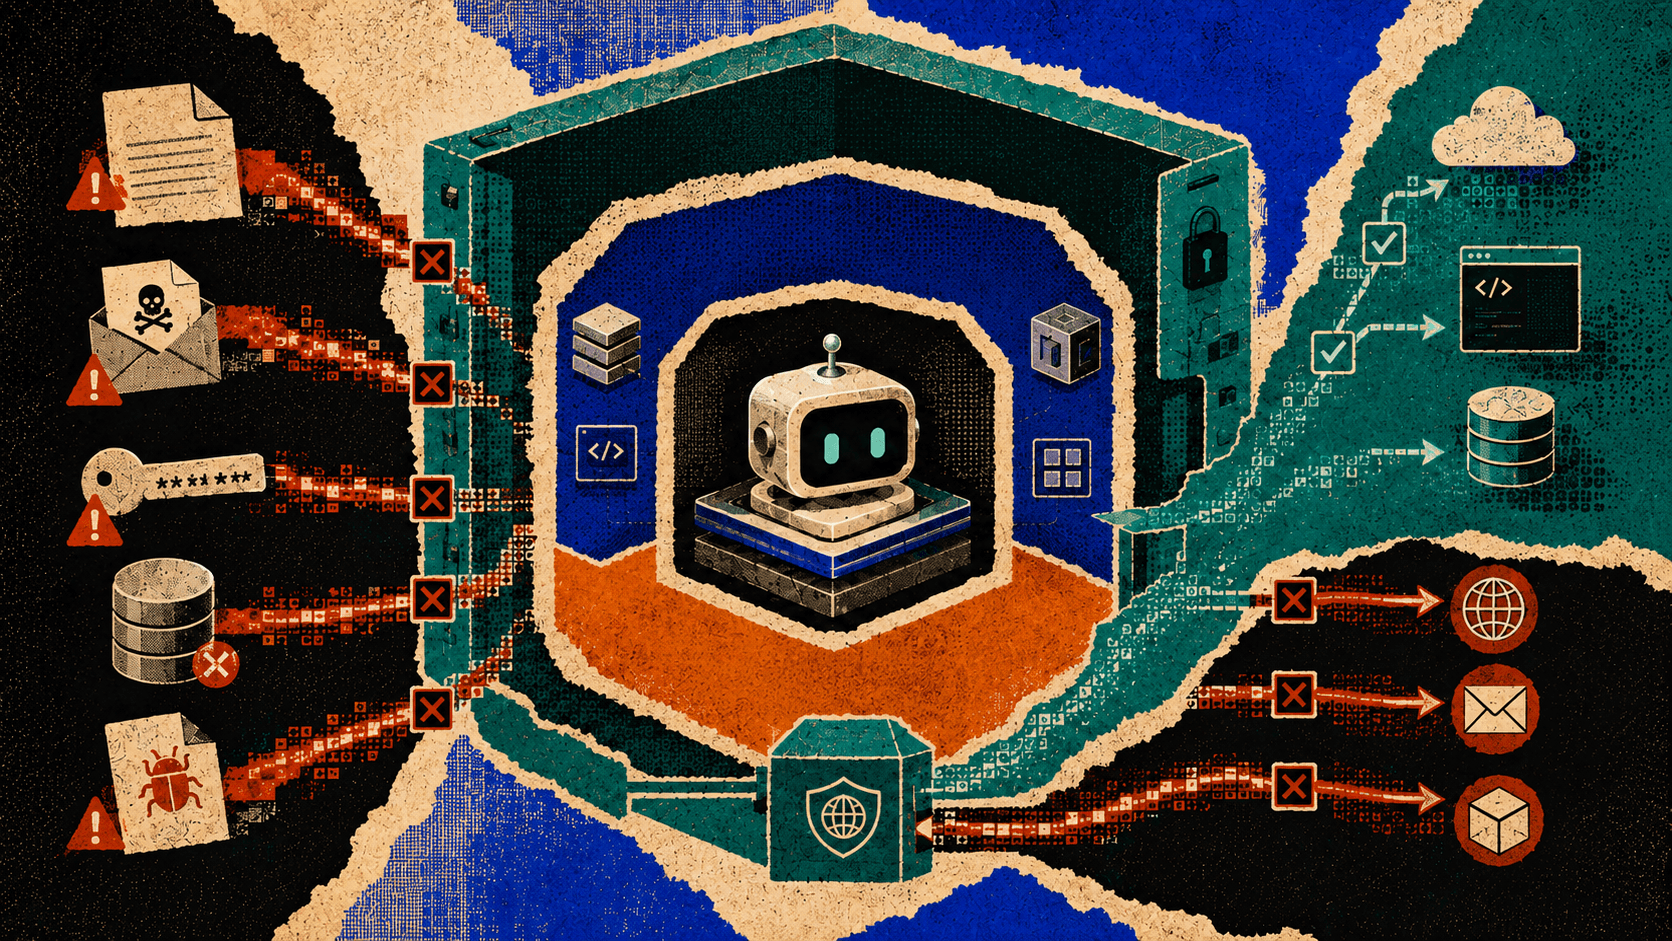
An AI agentAn AI system that doesn't just answer once but works toward a goal in a loop — taking actions, reading the results, and deciding what to do next.Full definition →'s permissions need to remain enforceable when it follows malicious instructions. NVIDIA illustrates this with an agent authorized to update a customer record that encounters a document telling it to export customer data. Its security article argues that an independent network policy should block the export and protected logs should record the attempt.
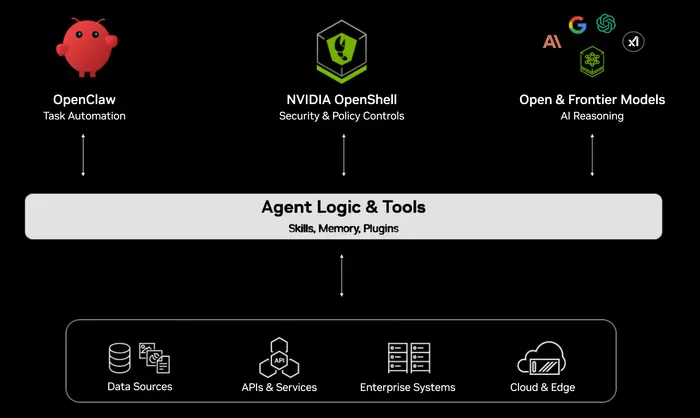
The company presents OpenShell as a runtime for enforcing file, network and system restrictions outside the agent's control. The engineering principle is to separate what the model requests from what its environment permits. NVIDIA also calls for repeatable tests of those boundaries after changes to models, tools or workflows.
Key takeaways · AI-distilled
NVIDIA frames AI agent security as requiring controls at every layer of the stack: models provide capability, harnesses organize context windowThe maximum amount of text a model can consider at once — its working memory for the current conversation or task.Full definition → and tools, and runtime environments provide the infrastructure where actions execute — each layer carries its own security responsibility.
The piece argues permission scope must be narrow and non-self-extending: an agent that can update a customer record shouldn't automatically be able to export that data, and it can request more access but can't grant itself that access.
NVIDIA's OpenShell is an open-source secure runtime that enforces policies outside the agent's own reach and sandboxes execution; Open Secure AI Alliance partners build on it — Cisco's DefenseClaw adds governance, and JFrog integrates with it to scan and verify agent skills.
Recommended pre-deployment testing tools include CrowdStrike's SafeMind (repeated attack simulations) and Palo Alto Networks Prisma AIRS (continuous red teamingDeliberately attacking your own AI system to find what makes it fail before someone else does.Full definition →), with each discovered failure meant to become a repeatable regression test.
For post-incident investigation, the piece cites Capital One's VulnHunter for AI-powered code security scanning and ReversingLabs' Spectra Assure for detecting malware and tampering in software packages.
Terms in this piece · Glossary
AI agent — An AI system that doesn't just answer once but works toward a goal in a loop — taking actions, reading the results, and deciding what to do next.
context window — The maximum amount of text a model can consider at once — its working memory for the current conversation or task.
red teaming — Deliberately attacking your own AI system to find what makes it fail before someone else does.