The quieter MCP risk: legitimate connectors with bad tool design
- Source
- writer.com
- Author
- WRITER
- Date
Context
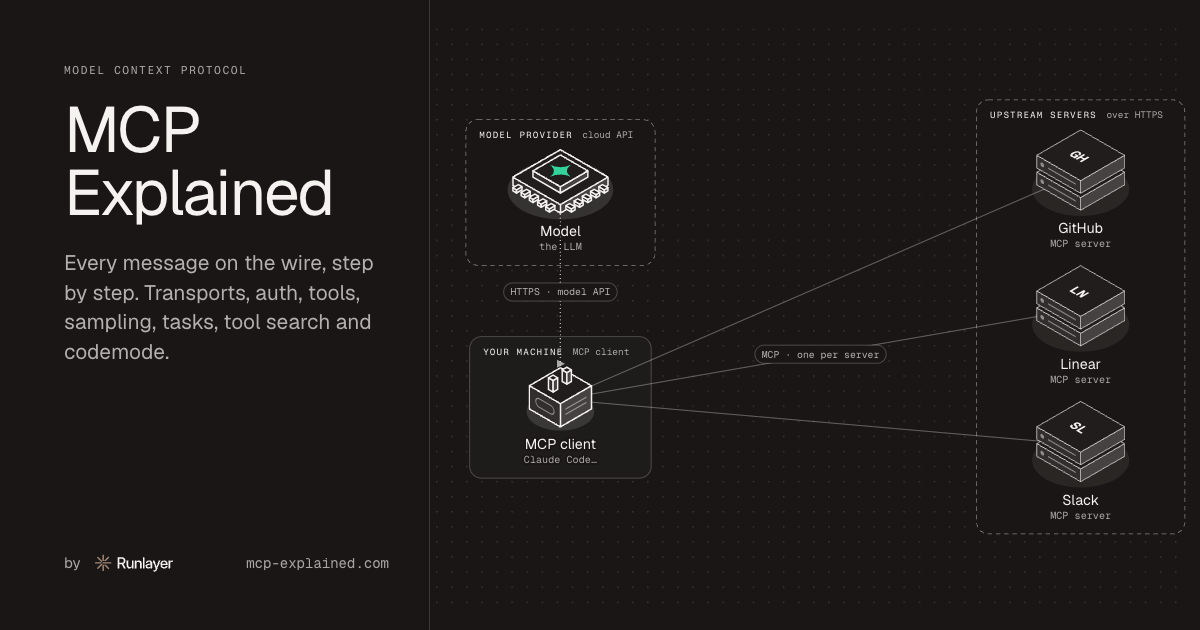
WRITER, a company that builds AI for businesses, argues that a connector usually leads an AI agent astray through bad tool design, not through an attack. In an engineering post, WRITER engineer Kapil Duraphe describes how the company's gateway screens for both problems. MCP, the Model Context Protocol, is a standard way for agents to use outside services. A connector packages one service as a set of tools the agent can call, and the gateway is the checkpoint a connector must pass before WRITER's agents can use it.
The security checks share one rule: do not take a connector's word for anything. A strict rejects any connector manifest with missing or undeclared fields. When an identity provider advertises the OAuth scopes it supports (the permissions a connector can request), WRITER treats that list as a claim to verify. For services it wraps itself, it requests only the scopes that the chosen tools need. A per-connector override can replace an advertised list with a hand-picked one, and the post says this often cuts the list by about 25%. Organizations can point custom connectors at any URL, so the gateway resolves each hostname and checks the address it actually leads to before calling it. That blocks DNS rebinding, a trick in which a hostname passes inspection with a harmless public address and then switches to an internal one. Each tool description also goes through a prompt- classifier before it enters the registry. The classifier looks for tool description poisoning, where instructions hidden in a description reach the model disguised as documentation.
The post's main point is the second failure, which WRITER says it sees far more often. A legitimate connector whose tools have vague descriptions, too many parameters or overlapping purposes, common when an API specification is converted directly into a connector, leads an agent to pick a plausible but wrong tool or guess at a parameter. According to WRITER, the same agent chooses correctly once the description says what the tool does. Its fixes are mechanical. The gateway keeps the labels MCP tools carry about whether a tool only reads data, deletes it, or is safe to retry. Each tool gets a deterministic name within its connector's namespace, instead of suffixes like create__1 that can swap places after a refresh. Fixed values an API requires, such as a pinned API version, are filled in automatically, so the model never has to guess them.
All of this is WRITER describing its own system and experience. The post offers no figures on how often each failure happens or how much the clean-up improves tool choice. The argument still applies to anyone connecting tools to an agent: passing a security review does not mean an agent can use a connector's tools correctly.
- Model Context Protocol (MCP) — A published agreement for an AI application to discover what a separate program offers and ask it to run one of those offerings.
- Schema — A written description of a data format: which fields exist, what kind of value each holds and which are required.
- Injection — A flaw where untrusted input is pasted into a command so that the input changes the command's meaning.
- Record — One unit of data in a file or table, such as one supplier's quote; distinct from a line of text.

Checking sign-in…
Loading comments…