Claude Security scanning moves to Mythos 5 in public beta
- Source
- x.com
- Date

Claude Security scans now run on Claude Mythos 5, available today in public beta for all Claude Enterprise customers. Put our most capable security model to work on your codebase, no separate model access needed.

Context
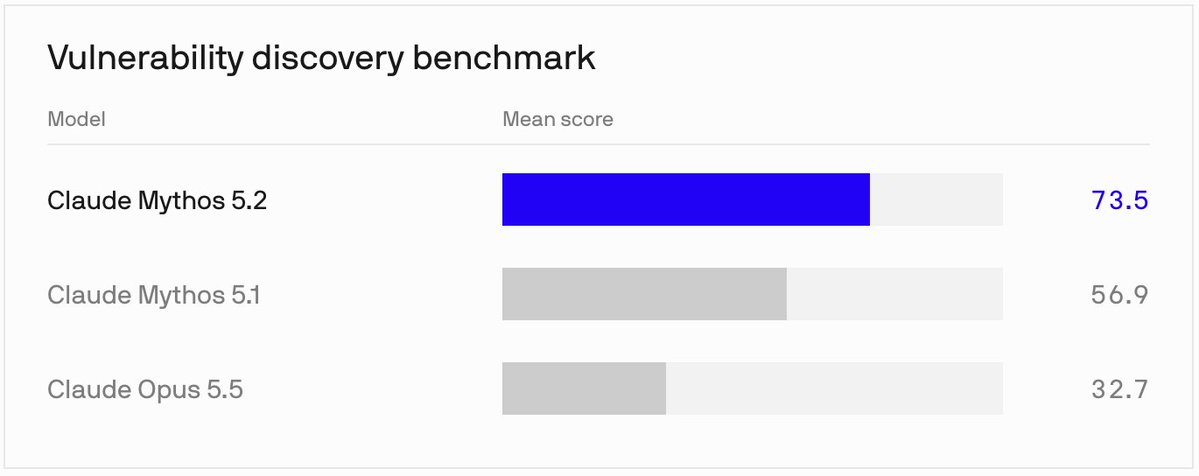
Claude Enterprise customers can now have their code scanned for vulnerabilities by Claude Mythos 5, which the Claude account calls Anthropic's most capable security , without being given access to the model itself. The announcement says Claude Security, Anthropic's code-scanning product, now runs its scans on Mythos 5 in public beta for all Enterprise customers. Anthropic's accompanying blog post says the scans are billed as ordinary usage under the existing plan, with no separate add-on.
The arrangement follows from how Anthropic weighs cyber risk. In the same post, the company says the riskiest situation is a user with direct access to a model, who could steer it toward harmful uses, while receiving only specific outputs such as a security alert or a patch carries much less risk. Claude Security fits the second case: it returns findings without exposing the model, and the post says the scan does not extend Mythos access to other surfaces.
The workflow is split in two. An admin enables Claude Security, a user picks a repository, and Mythos 5 scans it. Each finding comes with a CWE category (the standard catalog of software weakness types), confidence and severity ratings, and a suggested fix. Implementing a fix happens separately in Claude Code on the web, using whatever models the organization already has there, and Anthropic says every patch must be reviewed and approved by a person before it is applied. Anthropic's announcement does not include independent evidence of how well the scans find real vulnerabilities.
Checking sign-in…
Loading comments…