Claude Code Security
- Source
- anthropic.com
- Author
- Anthropic News
- Date
Context
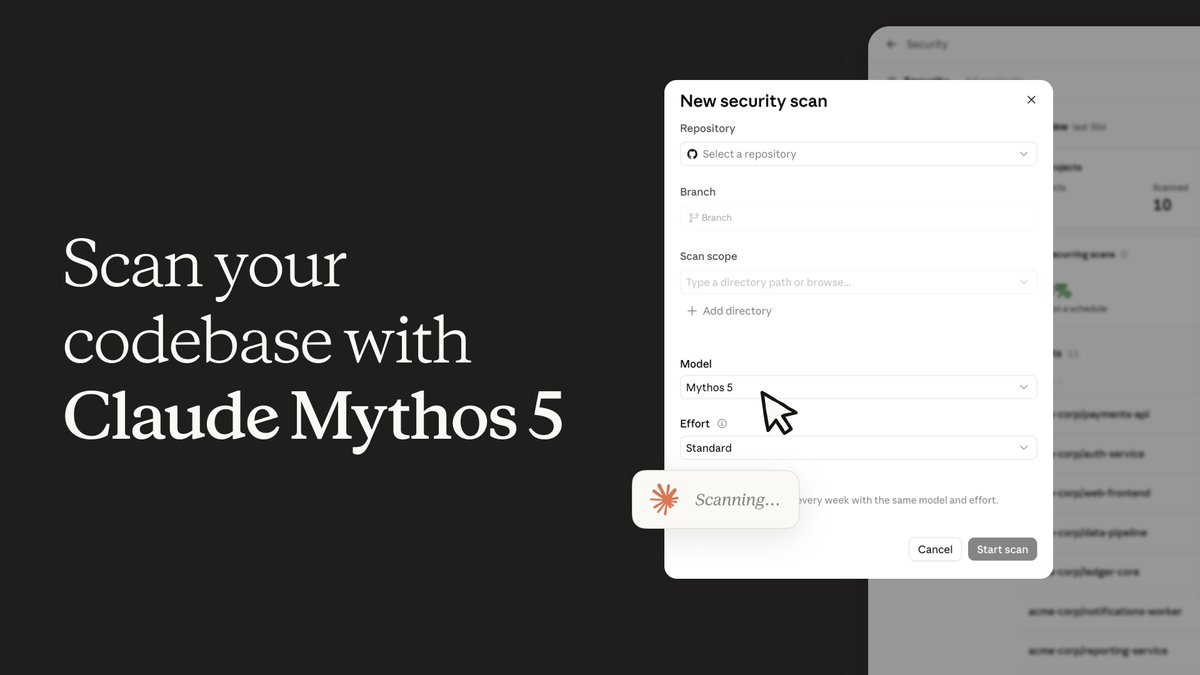
Anthropic describes Claude Code Security as a vulnerability-review workflow that follows interactions between software components and the movement of data through an application. In its February 20, 2026 announcement, it was a limited research preview for Enterprise and Team customers, with expedited access for open-source maintainers. The aim is to identify -dependent problems, including business-logic and access-control flaws that rule-based scanners often miss, and propose targeted patches for developers to inspect. February 2026 announcement.
Before a finding reaches the dashboard, Anthropic says the system re-examines it to try to prove or disprove it, filtering out false positives. It then supplies severity and confidence ratings alongside suggested fixes. Developers decide whether to approve a patch; the announced workflow does not apply one without human approval. That makes the output a prioritized set of findings and proposed repairs for review, described by the vendor without independent detection-rate evidence. Verification and approval process.
- context window — The maximum amount of text a model can consider at once — its working memory for the current conversation or task.
Checking sign-in…
Loading comments…