How to Carry User Identity Across Federated Kubernetes and AI Platforms
- Source
- developer.nvidia.com
- Author
- Elizabeth Goodman
- Date
Context
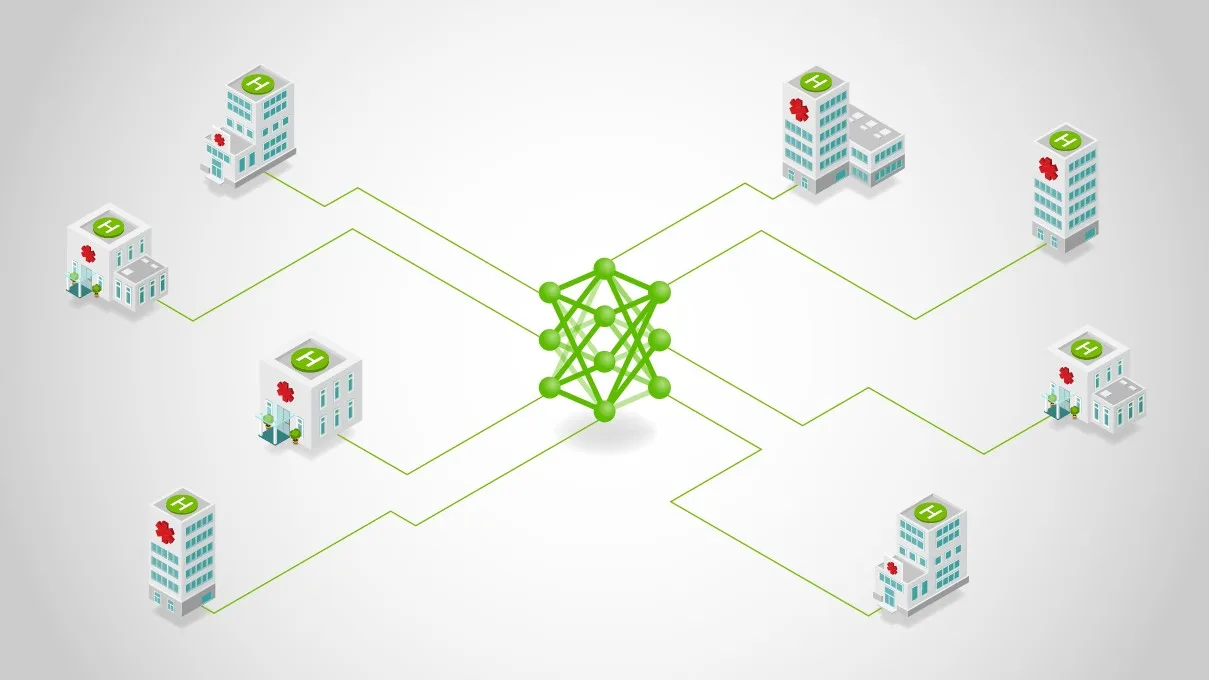
NVIDIA describes a way to carry a user's identity between tools without giving each application its own login session. A central gateway owns login, session renewal and logout. Regional gateways check that shared session before passing trusted identity information to local applications, while continuing to enforce local access policies. The architecture article explains this separation.
The company reports 55% fewer repeated login events across its internal developer platforms, without stating how the events were counted or compared. The broader design benefit is consistent session handling as users move between notebooks, datasets and assistants: applications consume a common identity interface instead of each implementing credential renewal and login integration.
 articleCode, Test, and Deploy on One Machine with NVIDIA RTX Spark
 articleHow to Rewrite Apache Spark UDFs for GPU Acceleration with AI Agents
 articleLower the Cost of Building and Running Visual AI Agents with NVIDIA VSS Blueprint 3.3
 articleHow SWE-Serve Exposes the Gap Between Local Tests and Live Serving
Checking sign-in…
Loading comments…