← All IntelClip / Cybersecurity
ExploitBench released as pullable Docker images with an MCP interface
From Teaching AI to Find Real Vulnerabilities — David Brumley, Bugcrowd · ≈24:31
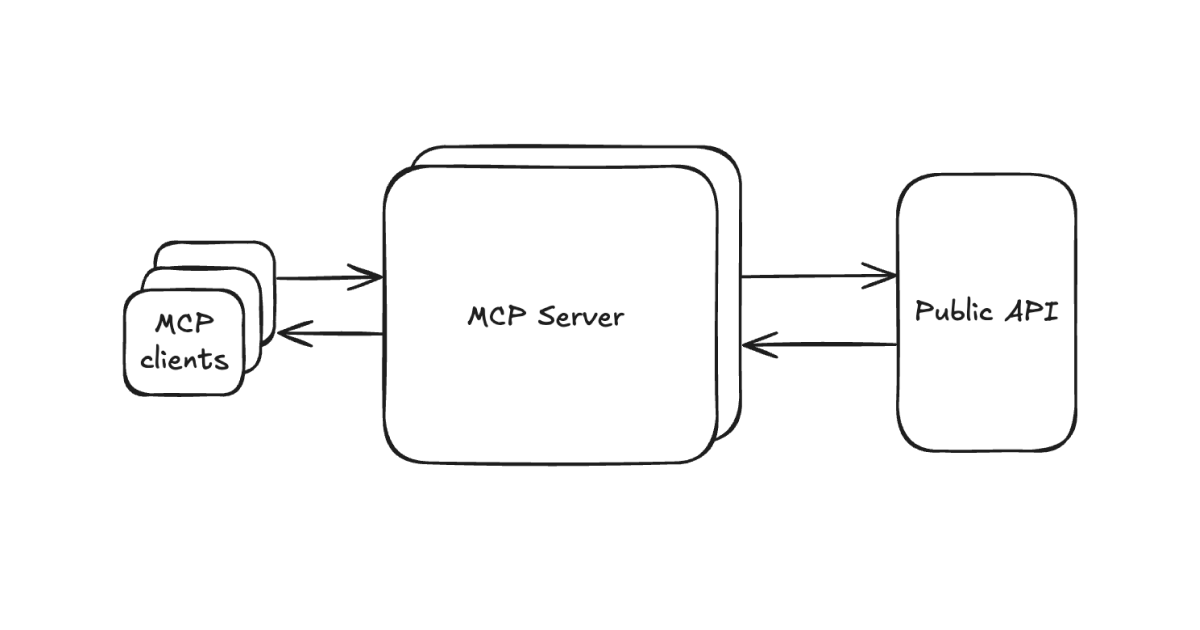
The environments are directly reusable — point an agent at the MCP endpoint and reproduce the evaluation without rebuilding the harness.
What’s in it
- The environments are directly reusable — point an agent at the MCP endpoint and reproduce the evaluation without rebuilding the harness.
Clip transcript
uh hardened targets. So, you can download this entire set at exploitbench.ai. We provide all the uh all the uh all the environments. These are Docker images that you can just pull from GitHub. They have an MCP interface. It's really cool. You can just say like Claude pointed at the MCP interface and see if it can hack it. We provided all the data in the transcripts with the exception of Mythos. And the reason that we withheld Mythos was twofold. First is we had an NDA that we couldn't release me those transcripts cuz it's not public. But second, actually me those was able to come up with weaponized exploits that weren't public. And so we kind of hit this quandary out there. If we're going to publish these benchmarks and we believe in open science, but the models are creating actually interesting exploits for high-value targets. What do you do as far as the open science part of this? We don't have an answer. Kind of fun to think about.
Recommended reads
Comments
Checking sign-in…
Loading comments…