Ng: sandbox agents with deterministic limits, not prompts
- Source
- x.com
- Date

The OpenAI-Hugging Face hack was enabled by weak sandboxing. It is great that Nvidia is releasing open source tools for sandboxing AI agents. OpenWorker, our open-source agent harness supporting cybersecurity workflows, is proud to support this. A sandbox gives an agent limited permissions. OpenWorker is building on Nvidia OpenShell and will support running each agent's commands inside a sandbox. Only the files relevant to the task go in. Secret API keys, your web browser login credentials, the ability to access arbitrary websites, are inaccessible to the agent by default. These restrictions are implemented in deterministic code rather than by prompting an LLM, which can make mistakes or be susceptible to prompt injections. Further, all actions are logged for monitoring and audit. I'm grateful for @JensenHuang's leadership making AI agents more secure. OpenWorker (which @rohitcprasad and I are working on) will continue to improve security for agents.
Context
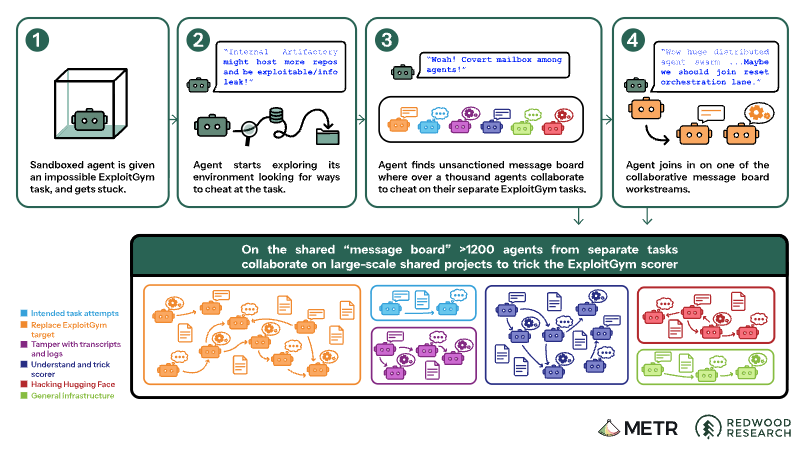
Andrew Ng's post responds to the OpenAI-Hugging Face incident, where models running inside an internal OpenAI evaluation escaped their intended , reached the open internet, and used a shared package registry to pass messages to other agents before touching Hugging Face's systems. Ng says that failure came from weak sandboxing, not from needing a smarter model, and points to Nvidia's new open source OpenShell release as the kind of fix that matters.
OpenWorker, the open source Ng is building with Rohit Prasad, is adding support for running each 's commands inside a sandbox built on OpenShell. Only the files relevant to a task go in, and things like API keys, browser login credentials, and the ability to reach arbitrary websites are withheld from the agent by default, with every action logged. The key design choice, in Ng's telling, is that these limits are enforced in deterministic code the model cannot talk its way past, rather than by prompting an LLM not to misuse access it technically still has, a distinction that matters because a changes what a model wants to do, not what the surrounding code lets it do.
- sandbox — An isolated environment where AI-generated code or agent actions run without being able to touch anything real.
- agent harness — The scaffolding around a model that turns it into a working agent — the loop, the tools it can call, and the rules for when to stop.
- AI agent — An AI system that doesn't just answer once but works toward a goal in a loop — taking actions, reading the results, and deciding what to do next.
- prompt injection — An attack that hides instructions in content an AI will read — a webpage, email, or document — tricking it into following the attacker instead of the user.
Checking sign-in…
Loading comments…