Why Hacktron hides full vulnerability details on public pull requests
- Source
- x.com
- Date

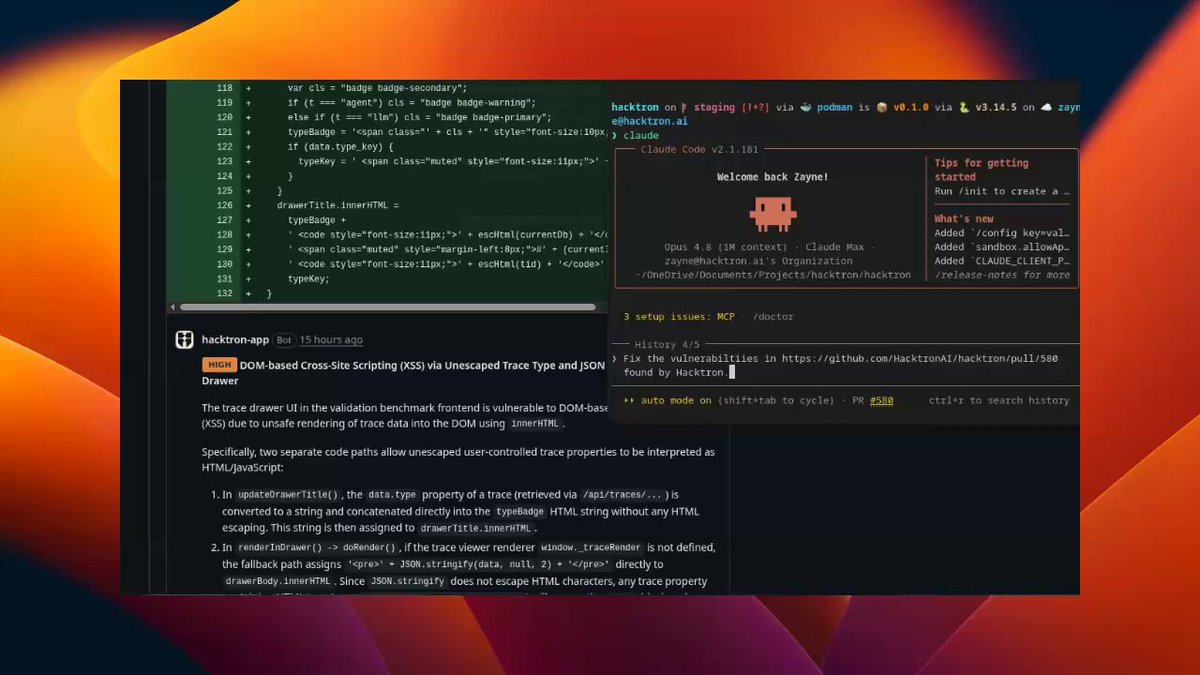
Almost every vulnerability we have exploited started as a pull request someone approved. That means your pull requests are not just code review events. They are security events too. Think about an open source project. A scanner finds a vulnerability and posts it right there as a public comment on the pull request: the full title, the description, the exact file and line. Great for the maintainer who has to fix it, but it’s also great for any hacker lurking around. The bug has been published before even closing it. So on public repos, Hacktron handles security issues differently. For findings outside the code a PR actually touched, the public comment shows only a link to view the details within the Hacktron platform. The real details stay private, visible to only the maintainers. Private and internal repos show full details as normal.

Check out our open-source program: https://t.co/4Hz87dc5hF
Context
Hacktron builds an automated tool that reviews pull requests for security problems and posts findings as comments. In a thread explaining its disclosure policy, Hacktron AI says almost every vulnerability its team has exploited started as a pull request someone approved, so it treats PRs as security events, not just code review. The problem it identifies: a scanner that posts a full vulnerability title, description, and exact file and line as a public PR comment helps the maintainer fix it, but it also hands the same details to anyone else reading the public repository before the bug is fixed. For findings outside the code a given PR actually touches, Hacktron's public-repo comments now show only a link into its own platform, where the full description stays visible to maintainers alone; private and internal repositories still get the complete comment as before.
Checking sign-in…
Loading comments…