Introducing Vercel Security Review
- Source
- vercel.com
- Author
- Nate McGrady
- Date
Context
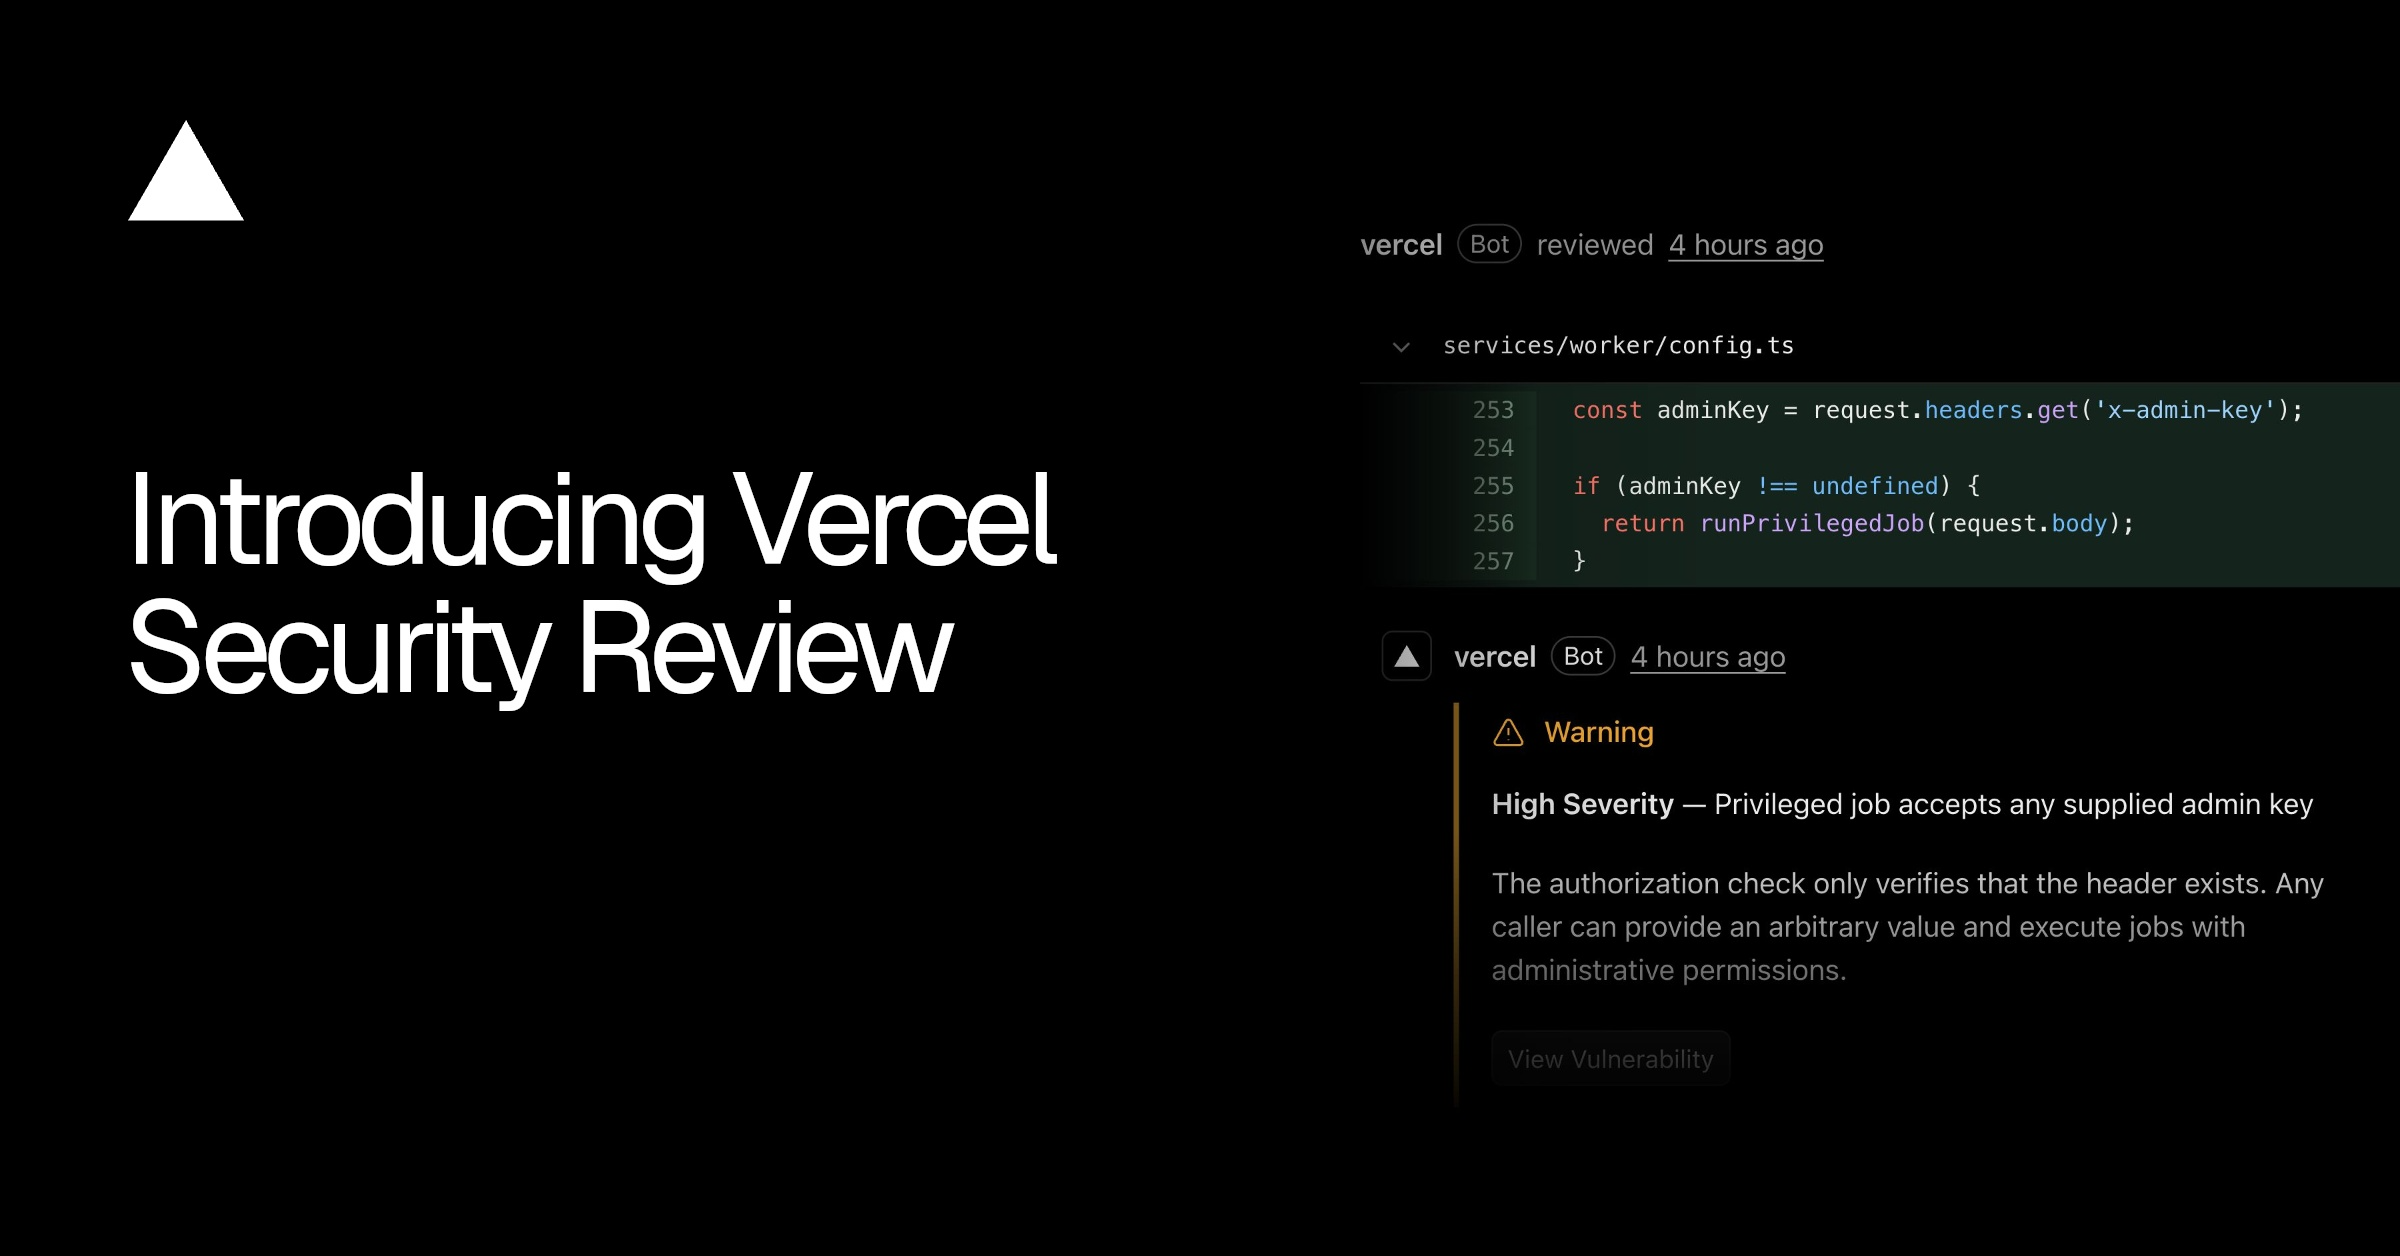
Vercel now offers an AI reviewer that checks every push to a connected GitHub repository for security flaws. Vercel Security Review, in public beta for Pro and Enterprise teams, is a new part of Vercel , the AI assistant built into Vercel's hosting platform (expanded in July). Once a team enables it, each push, including a direct push to the production branch, triggers a scan of the changed code for problems such as missing authorization checks or exposed secrets, according to Vercel's announcement.
The reviewer looks only at what changed. Each review compares the push against a base, which for deployments is the branch's previous deployment, and Vercel says that limiting the scan to the diff lets it finish in seconds and run on every preview and production deployment. The agent reads the diff with its surrounding code, traces how the changed code can be reached, checks for protections already in place and rechecks each finding before reporting it. Vercel's example is an invoice download endpoint that looks up an invoice by ID without checking which organization owns it, so any signed-in user could download another organization's invoice by changing the ID. Vercel says this tracing is how the agent catches logic flaws that pattern-matching scanners miss. The announcement publishes no detection or false-positive rates, so that is a description of the method, not a measured result. Teams can also add policies written in plain language, for example requiring any endpoint that returns customer data to check that the requester owns it.
Findings go to a Security dashboard, and on private and internal repositories also to a GitHub check and a pull request comment. Each finding is checked against earlier ones so it is not reported twice, tied to the deployment where it first appeared, and flagged in production too if the vulnerable change is merged there. Where Vercel Agent can fix a finding, a team can click Fix with Vercel Agent; the agent then confirms the flaw still exists, makes the smallest change that fixes it and updates the tests. Alternatively, a team can pull findings through the vercel security vulnerabilities command and hand them to its own coding agent.
Reviews cost the Vercel Agent rate: model at the provider's price plus $0.25 per million tokens, with reviews free until November 10, 2026; fixes made with Vercel Agent are billed at that rate. The beta covers only code pushed to GitHub. Vercel says deployments from its CLI and v0, and repositories that do not deploy on Vercel, come next.

Checking sign-in…
Loading comments…