Now in research preview: Codex Security Review It takes a deeper look at GitHub
- Source
- learn.chatgpt.com
- Author
- OpenAIDevs
- Date

Context
OpenAI's Codex Security Review assesses a pull request's changes alongside repository and any configured threat model, a description of an application's assets, trust boundaries, security assumptions and specific risks. That gives the security review context beyond the changed lines themselves. The documentation explains how teams can supply this context.
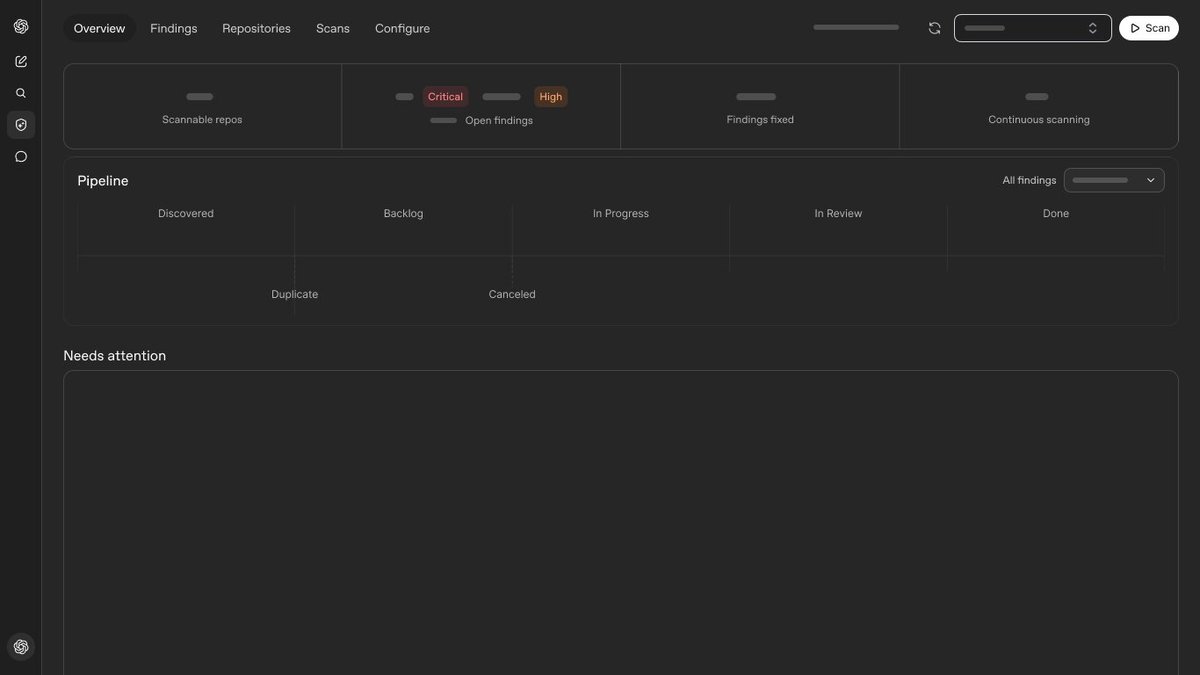
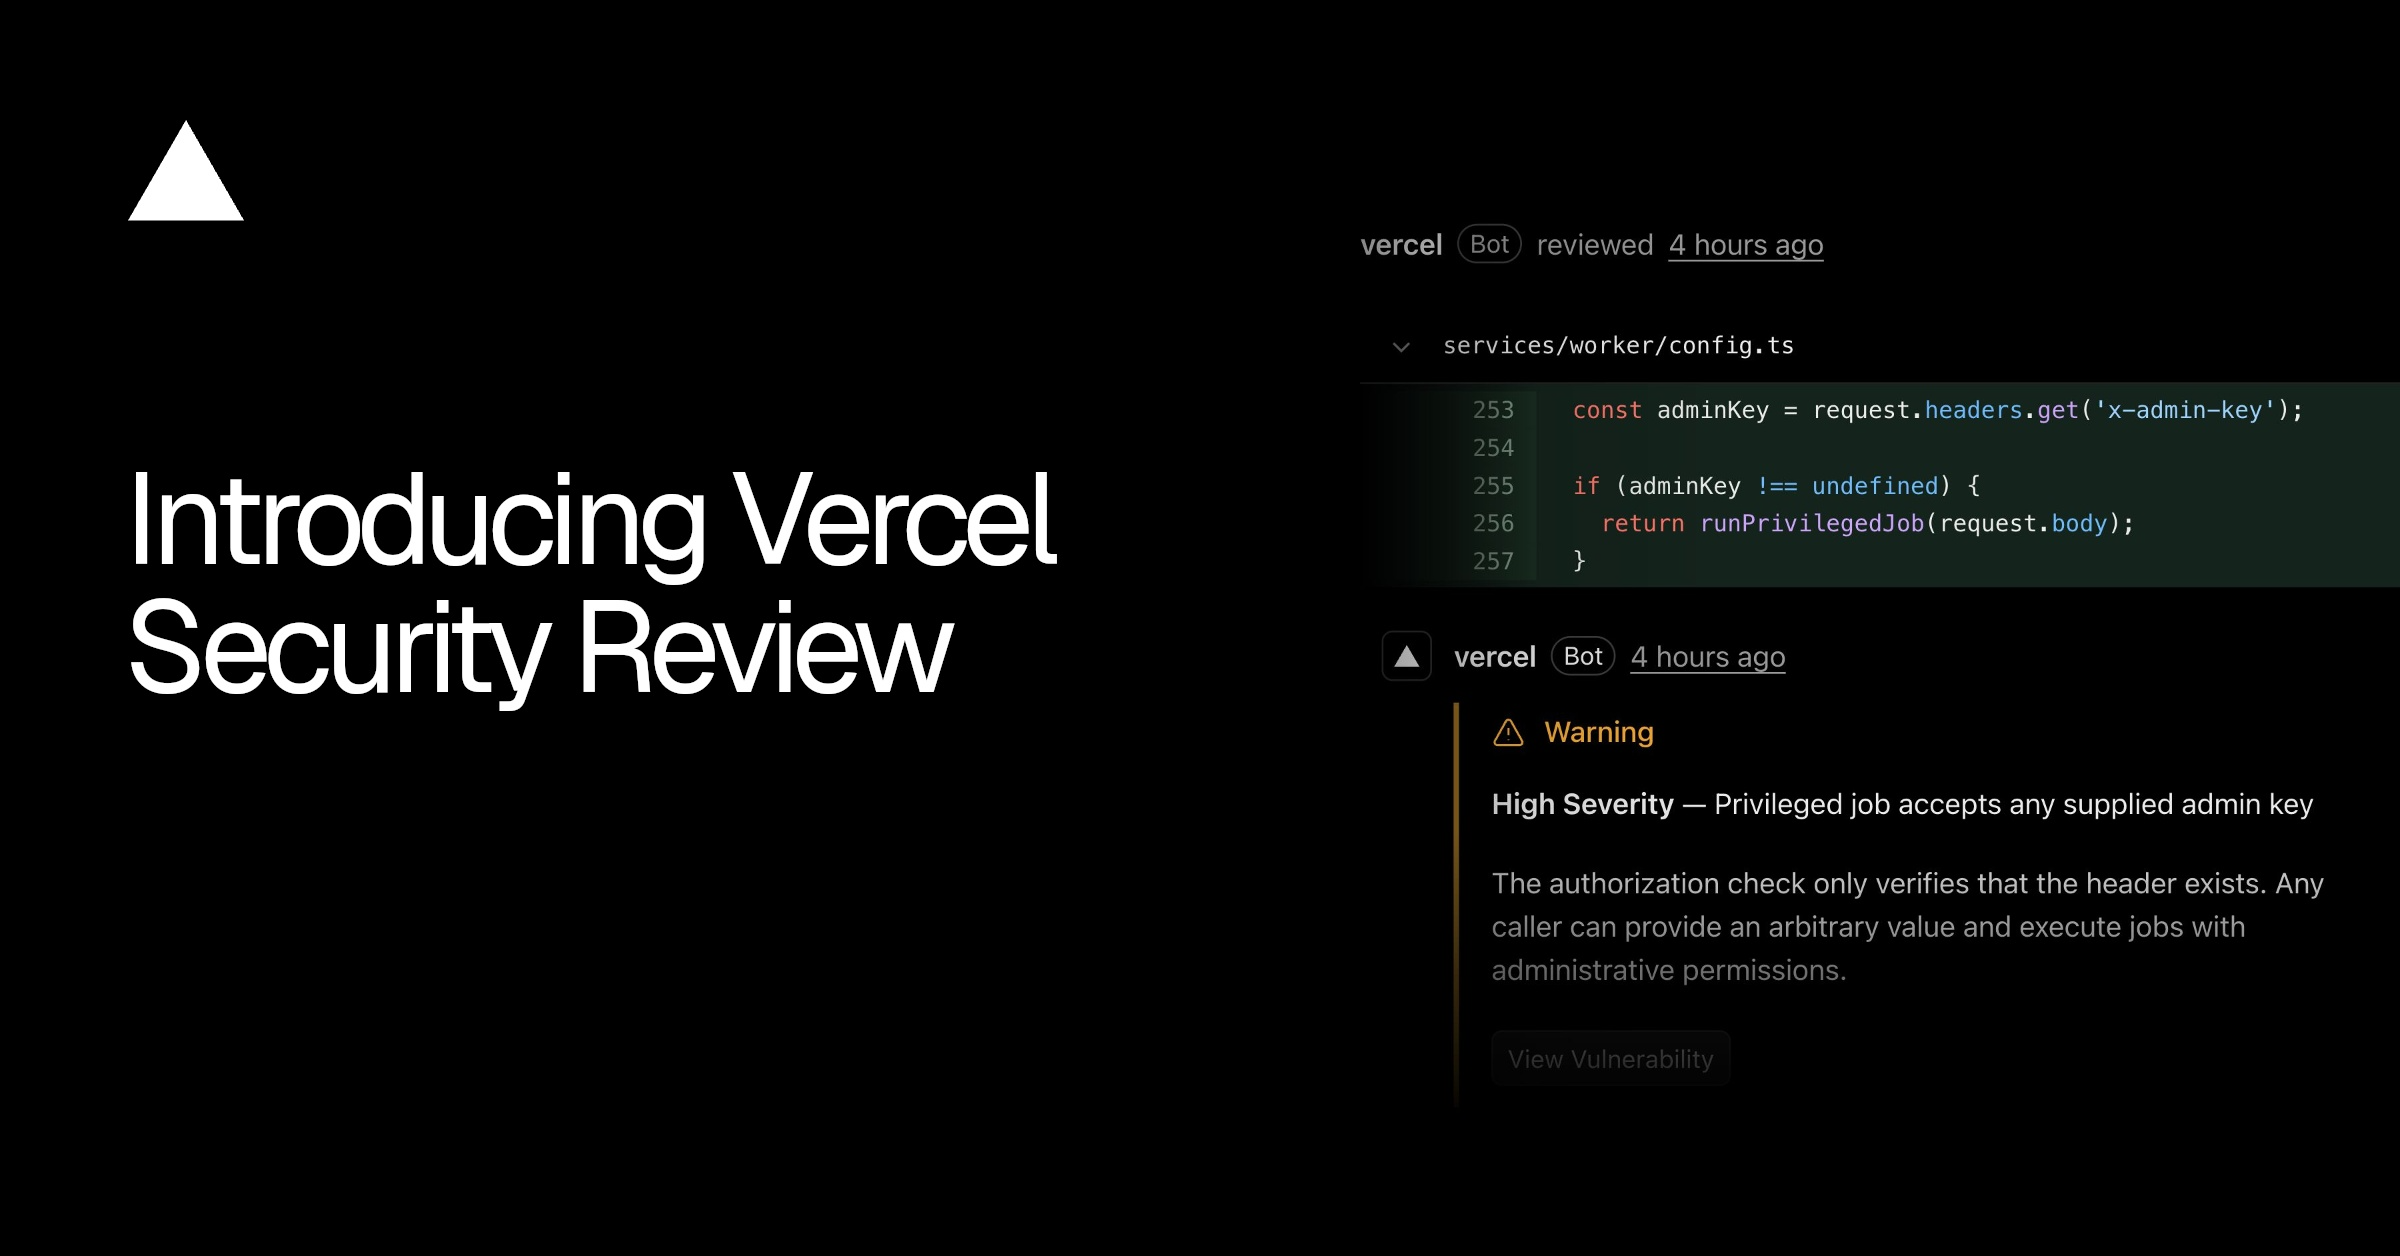
The comments on a GitHub pull request show only findings that meet the configured reporting threshold. Automatic reviews default to High and Critical findings; manual reviews also include Medium. The full report remains in Codex, so an empty comment thread means no findings met the posting threshold, rather than establishing that the change is secure.
- context window — The maximum amount of text a model can consider at once — its working memory for the current conversation or task.
“During the introductory period, Codex Security Review does not consume ChatGPT credits.”
OpenAIDevs
“Codex Security Review goes deeper than Code Review on security-specific risks by analyzing the pull request diff, supporting repository context, and configured threat models or security guidance.”
OpenAIDevs
“By default, automatic Codex Security Reviews report High and Critical findings, while manually requested reviews report Medium , High , and Critical findings.”
OpenAIDevs
“If you do not specify a source, Codex regenerates the threat model for every review.”
OpenAIDevs

Checking sign-in…
Loading comments…