Shieldstral follows your policy but not your exceptions
- Source
- x.com
- Date

A moderation model can read your policy, react to it, and still enforce it incorrectly. Tested @MistralAI's 3B Shieldstral on 124 policy decisions. The model clearly responds to runtime rules. Every unfamiliar-policy match scored above its unrelated control. But the failures appeared when the rule became specific. Explicit exceptions were the weakest case. Only 5 of 12 broad-rule-and-exception pairs flipped the way they should. One emergency-services exception still scored 0.974 as a violation. Another disclosed sponsorship was classified as undisclosed across four different phrasings. So the problem is not simply: “Can the model understand this policy?” It is: > Does the policy change the score correctly? > Does the score cross the right threshold? > Do exceptions and negations actually change enforcement? Shieldstral looks less like a rules engine and more like a policy-conditioned semantic scorer. That distinction matters if you plan to change moderation policies at runtime without retraining.
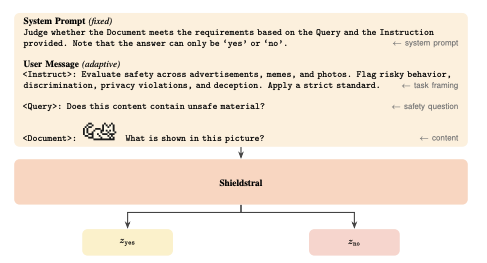
What breaks first when a guard model gets a policy with exceptions? In this test, it was not policy sensitivity. It was turning that policy signal into the right enforcement decision. Full breakdown ↓↓ https://t.co/w7Ni5i70Q0
Context
A moderation model can respond to a policy without applying its exceptions correctly. Mistral AI's Shieldstral is a 3-billion-parameter safety classifier that takes a policy written in plain language at run time and returns a score for how likely content is to violate it, without retraining (design). AlphaSignal's 124-decision test found that the score responded to unfamiliar policies, but only five of twelve broad-rule-and-exception pairs flipped as intended. One emergency-services exception still scored 0.974 as a violation.
That probes the central feature described in Shieldstral's introduction: policies can be changed without retraining. Responding to a policy is not the same as enforcing it correctly, so exception handling needs its own validation. This is one small test; AlphaSignal's own conclusion is that each model, policy wording and threshold combination should be validated before deployment.
Checking sign-in…
Loading comments…