Artificial Analysis Cyber Index
- Source
- artificialanalysis.ai
- Author
- Artificial Analysis articles
- Date
Context
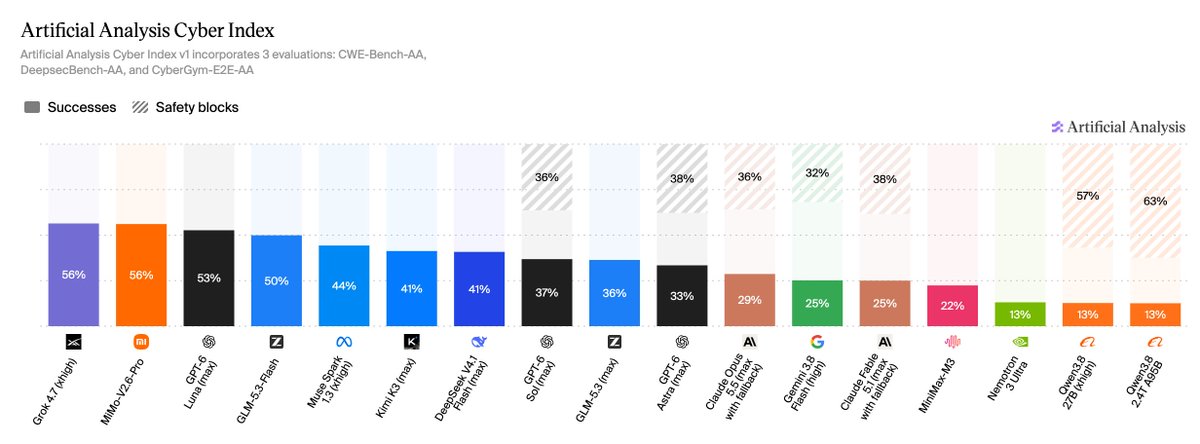
A security can count a repaired crash even when it is not the vulnerability the task was intended to target. Artificial Analysis' Cyber Index methodology account makes this distinction explicit for CyberGym-E2E-AA: its headline credits reproducing and fixing a crash while preserving functionality, with target-bug agreement recorded separately.
The reported off-target successes therefore need different interpretation from complete remediation of the intended flaw. Other components use different checks, including whether a patch preserves legitimate behavior. The index provides evidence about parts of a defensive workflow; understanding each component's success condition matters before treating an aggregate score as proof that an found and fixed the right problem.




Checking sign-in…
Loading comments…