Hardware-Rooted AI Security That Won’t Slow You Down
- Source
- developer.nvidia.com
- Author
- Elizabeth Goodman
- Date
Context
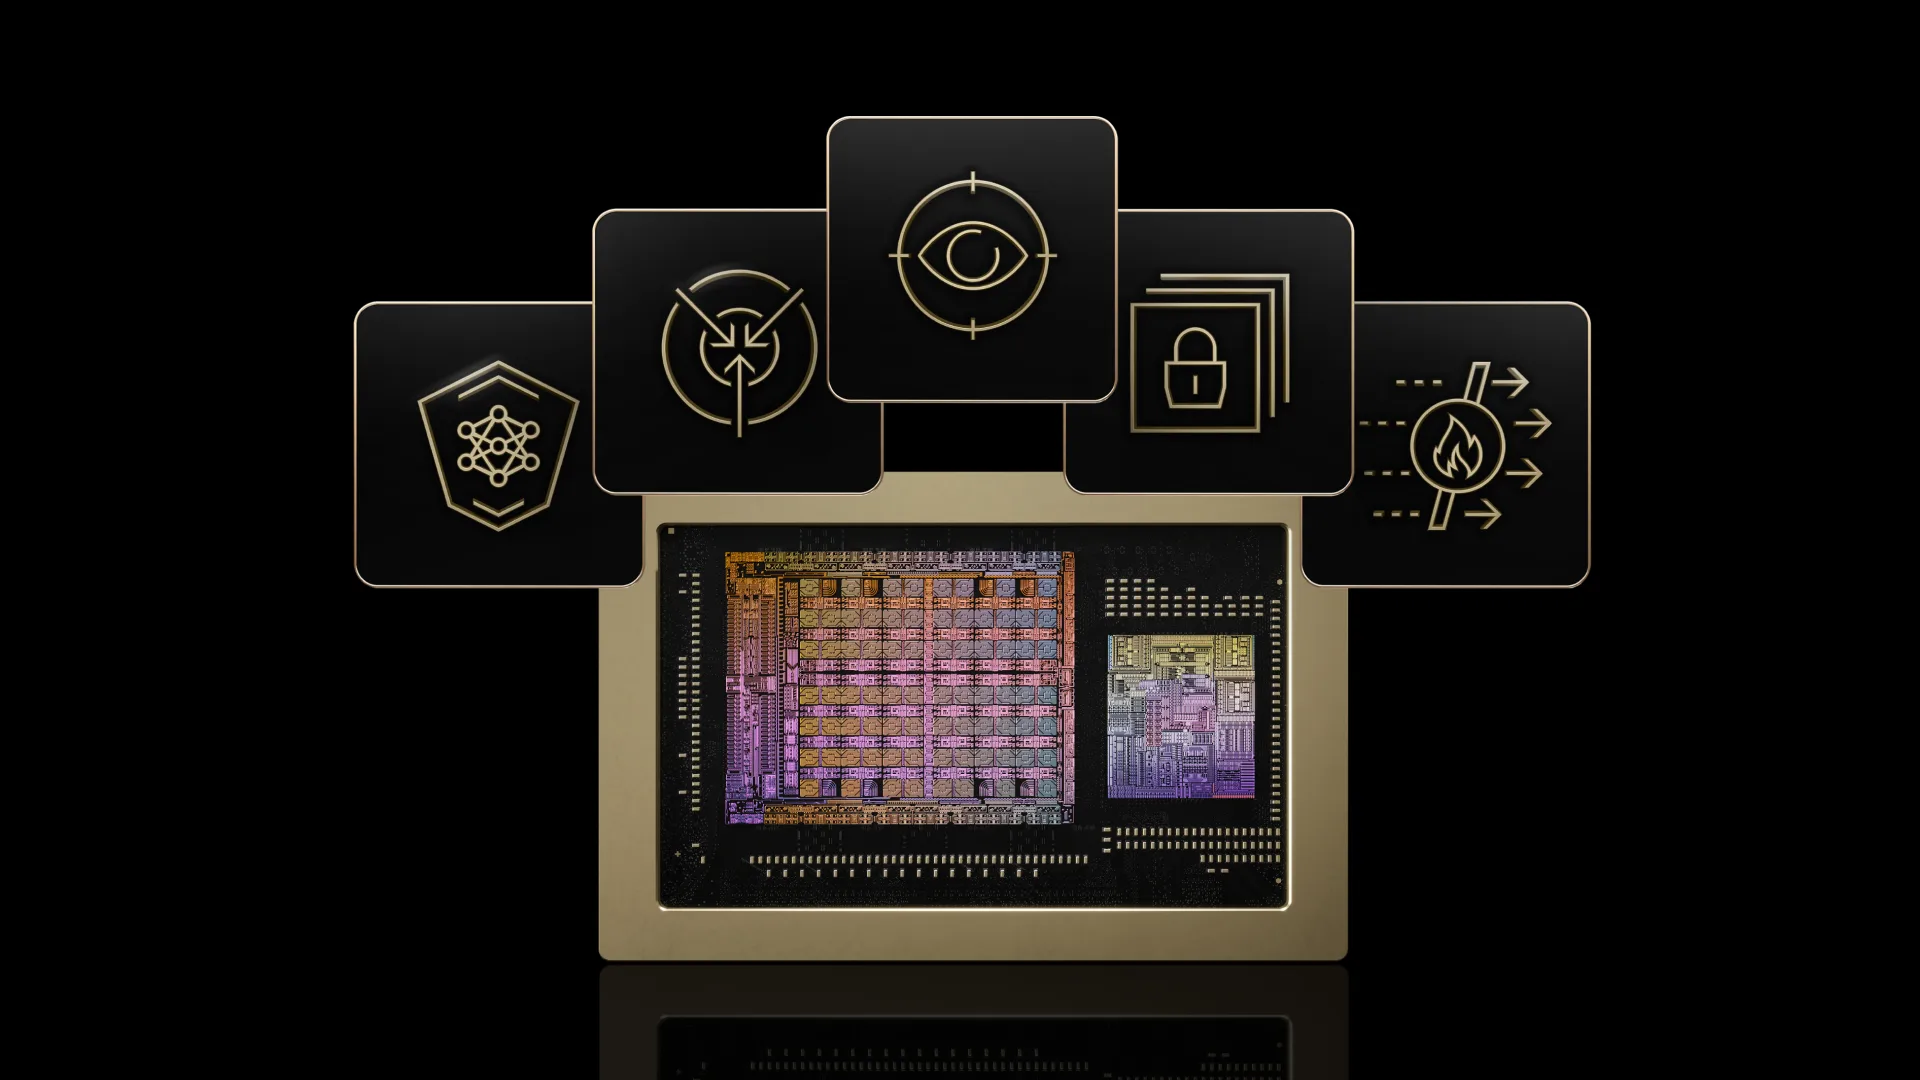
NVIDIA's confidential-computing design protects sensitive model data during and checks the execution environment before releasing secrets to it. Remote attestation compares signed hardware and system measurements with an expected reference. Model decryption keys can then be supplied to the verified environment. That protects data and code in use; it does not show that the application itself is safe. The article explains this sequence.
The performance cost was small in the reported test but not zero. On HGX B300 hardware running Qwen 3.5 397B-A17B at FP8 precision with SGLang, NVIDIA's table reports throughput reductions of 1% to 7.5% with confidential computing on versus off. Those results support a bounded claim for the tested configuration only. The benchmark table and setup supply the conditions.
 articleHow NVIDIA OpenShell Reference Architecture Secures and Governs AI Agent Workloads at Scale
 articleCode, Test, and Deploy on One Machine with NVIDIA RTX Spark
 articleHow to Rewrite Apache Spark UDFs for GPU Acceleration with AI Agents
 articleLower the Cost of Building and Running Visual AI Agents with NVIDIA VSS Blueprint 3.3
Checking sign-in…
Loading comments…