Numbat brings pre-execution blocking and audit to any agent harness
- Source
- x.com
- Date

Today we’re open-sourcing Numbat, an agent-detection and response layer that is designed to work across agent harnesses. Numbat gives security teams visibility into agent activity, with controls to block selected actions before execution. Read more: https://t.co/LVhkCJ2sMt
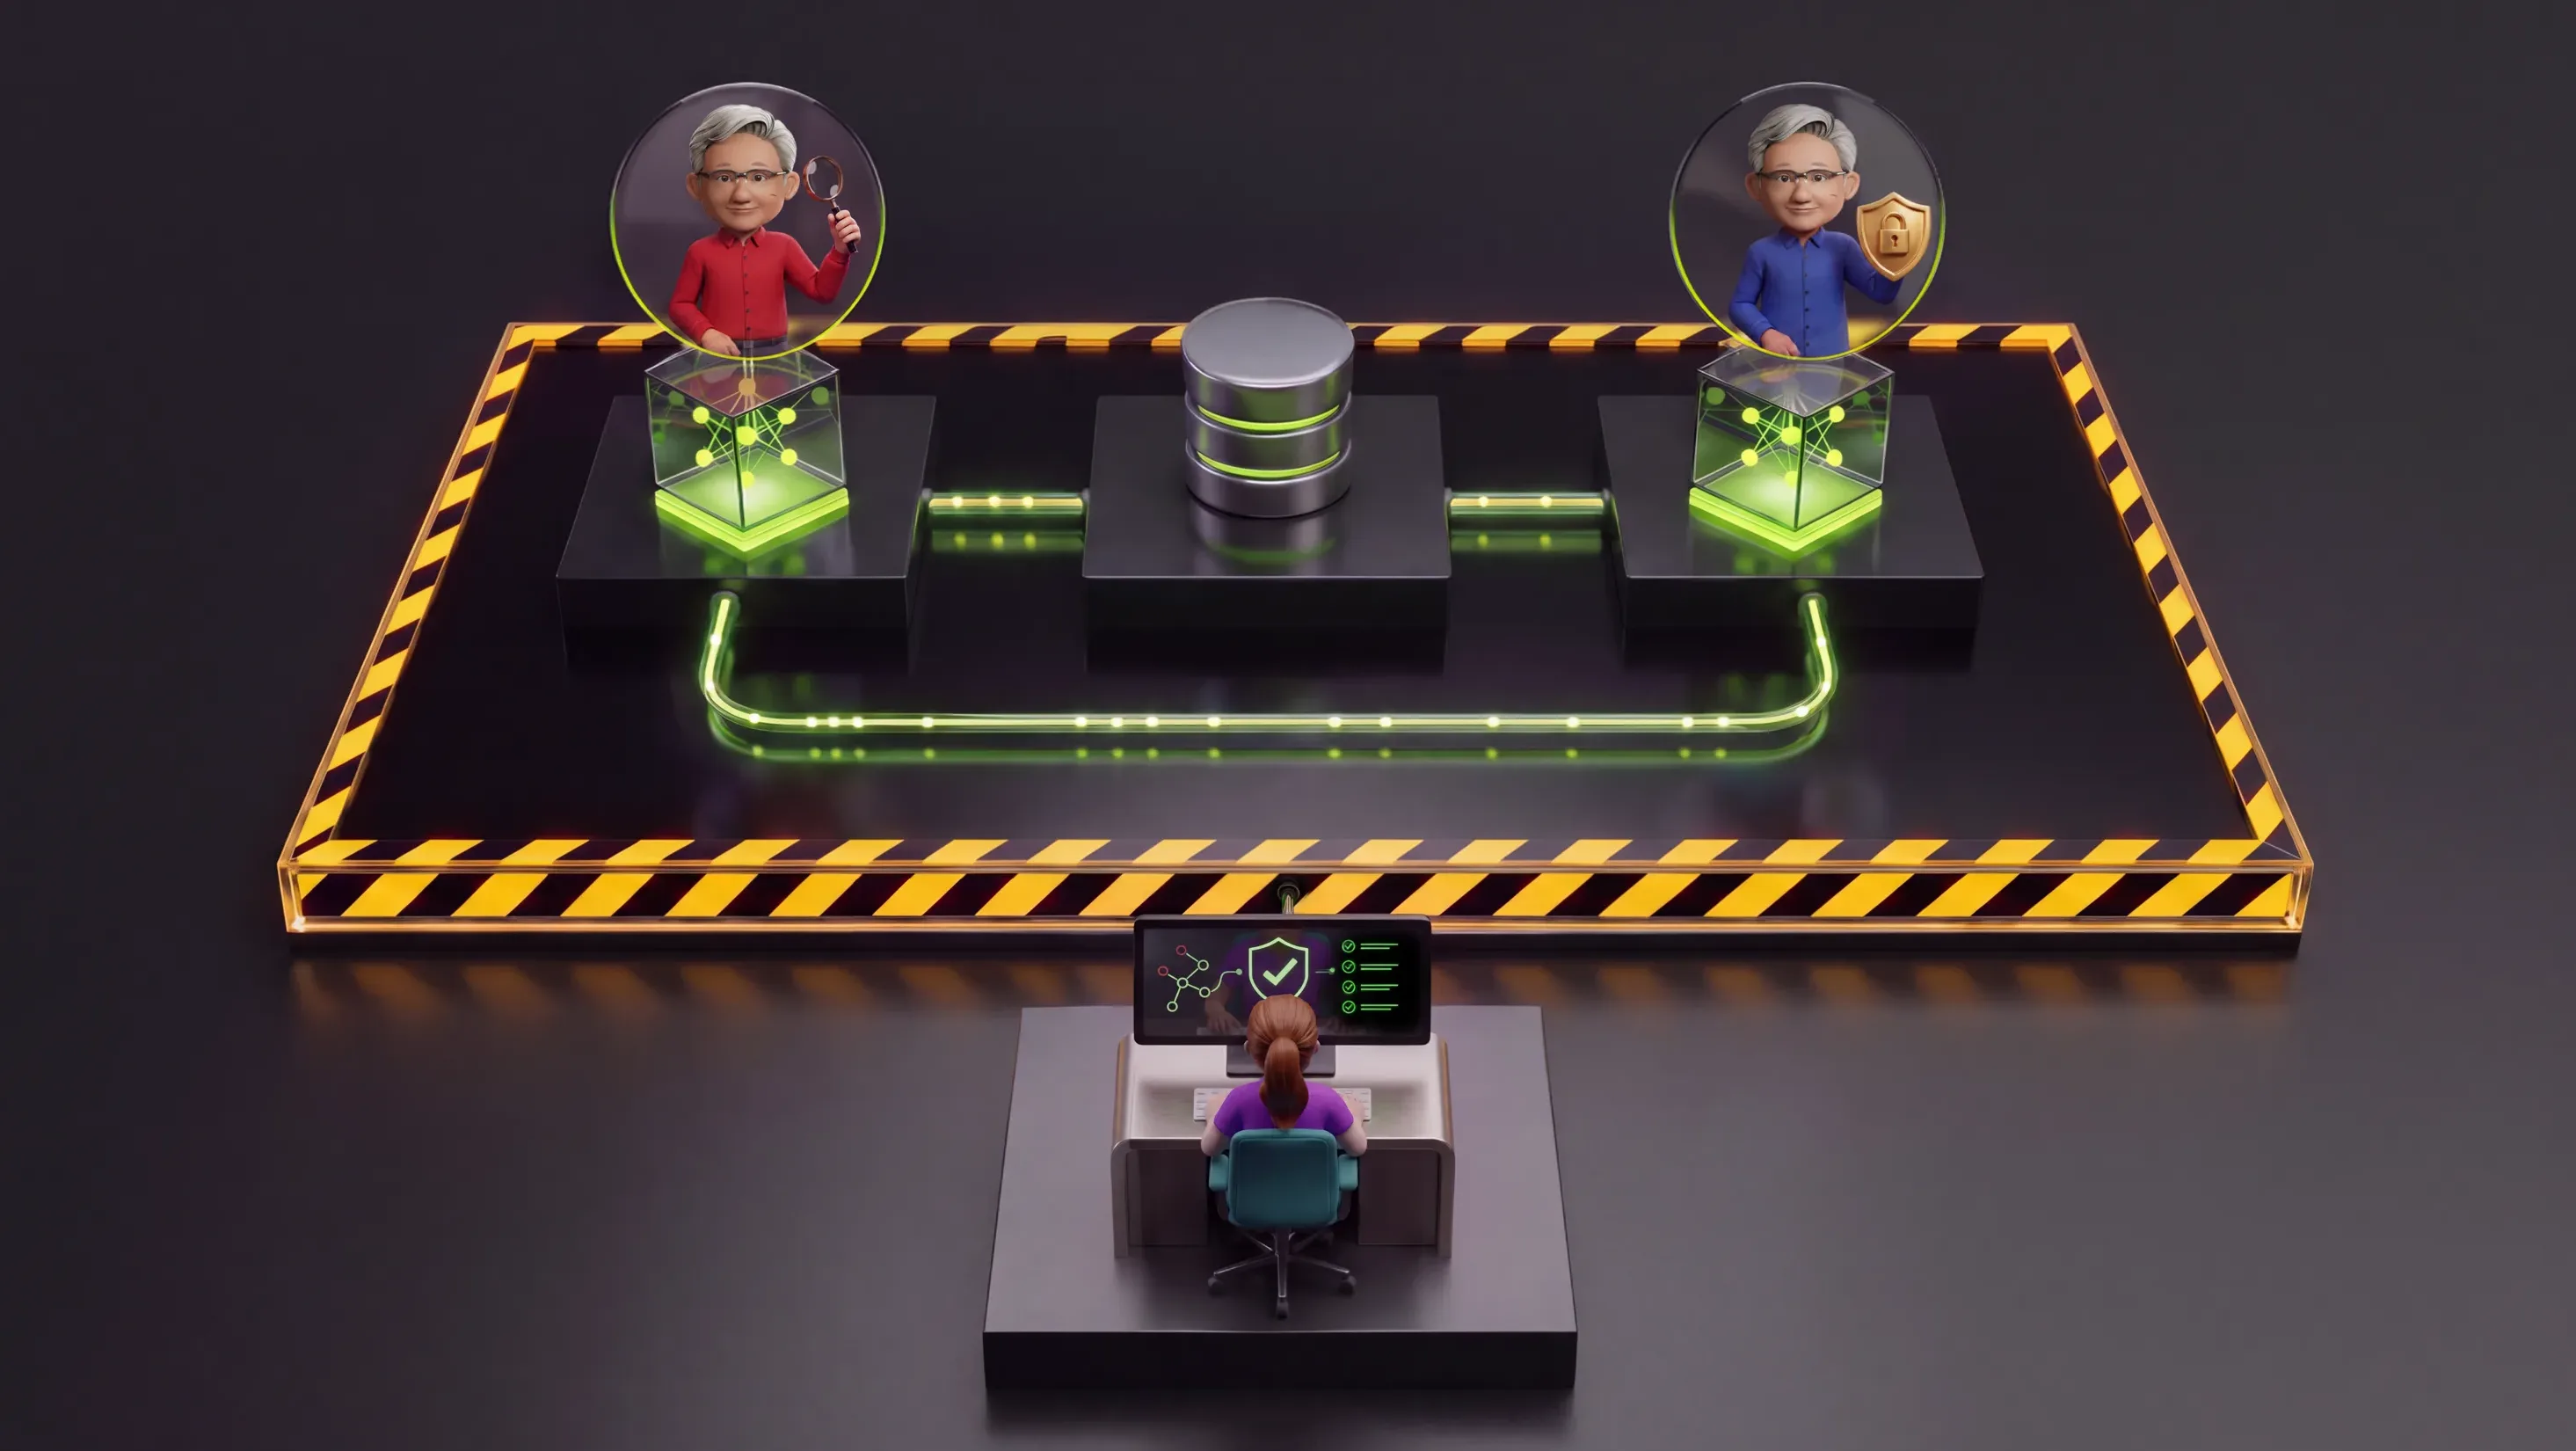
Numbat works across agent harnesses on desktop, CLI, IDE, and gateway agents. It supports live monitoring, local detection, pre-action blocking, and forensic reconstruction from existing session artifacts.

Numbat runs across our systems and sends audit events, findings, and security alerts to Computer. Computer continuously analyzes this telemetry, escalates suspicious behavior, and proposes new on-device detections for Numbat, creating a continuously improving detection flywheel.
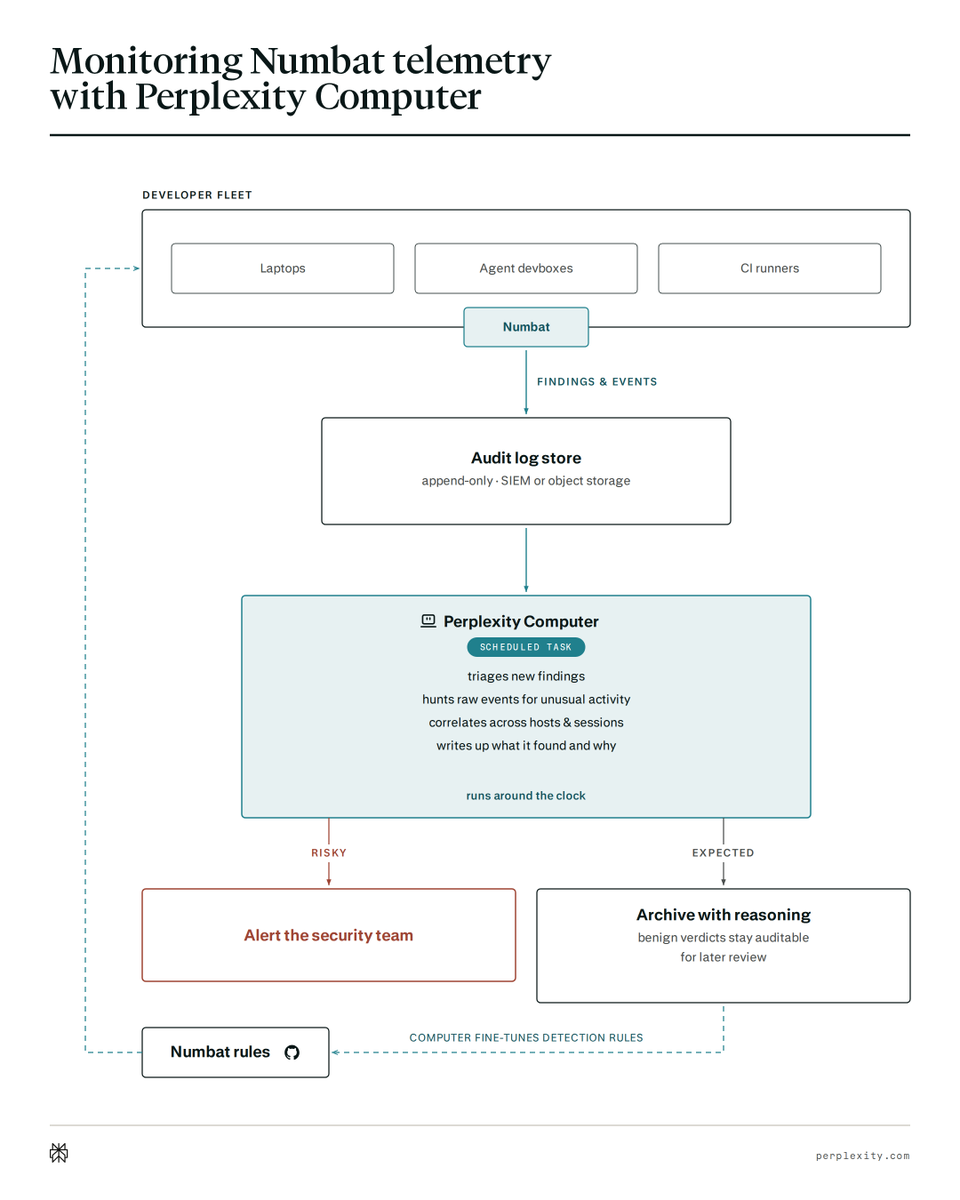
Numbat ships as a single Go binary for macOS, Linux, and Windows. Available now under Apache 2.0: https://t.co/mAmU22Vhzn
Context
Perplexity's Numbat adds security checks around an 's actions. It integrates with supported agent software through hooks, which run checks at defined points in execution. Where pre-action hooks allow intervention, Numbat can block an action that matches a security rule before it runs. Its technical account also describes reconstructing activity from stored session records.
These functions serve different needs: immediate rules can stop recognized behavior, while a consistent activity timeline helps investigators examine incidents afterward. Inside Perplexity, Computer analyzes those records and proposes detection changes, but the described process sends the changes through human review before deployment.
- AI agent — An AI system that doesn't just answer once but works toward a goal in a loop — taking actions, reading the results, and deciding what to do next.
Checking sign-in…
Loading comments…